The creation of the said tech office signals the Defense Department’s intent to ramp up a range of aggressive covert activities abroad, according to officials and records. [1][2]
Origins and Leadership
TSO was created by reorganizing two classified Pentagon intelligence programs that have conducted smaller-scale clandestine tech-sabotage efforts since 2023, according to previously unreported Defense Department records and memoranda.
Mission and Operations
TSO lacks legal authority to conduct clandestine operations directly but works with senior military and intelligence officers to develop tools and strategies to disrupt adversaries’ access to critical defense technologies, officials said. Its staff includes engineers, special operators and intelligence officers; work ranges from building hacking tools to planning deception operations that trick adversaries into installing faulty components in foreign weapons platforms. [1][3]
A former U.S. intelligence official who worked closely with the agency said its goal is to “buy time or stop adversaries from developing technologies” that would most threaten the U.S. military in a major conflict. The office’s creation signals intent to expand covert activities abroad, potentially including cyberattacks, supply chain disruptions and disinformation operations, according to officials and records. [1][4]
The Pentagon has spent months quietly building an elite new tech agency to help covertly disrupt and sabotage foreign technology programs considered threats to American military superiority, according to the POLITICO report. [5][6]
Budget, Contractors and Bureaucratic Friction
It is unclear how much money has been allocated to TSO or whether it has issued new contracts, according to the report.
Special Operations Command and U.S. Cyber Command objected to creating the agency over concerns it would cut into their budgets, according to two former intelligence officials and one former senior national security official.
Oversight and Secrecy Concerns
Some officials said the secrecy could make it harder for Congress to identify potential impropriety in TSO’s operations or contracting; only a small number of congressional staffers have been read in, a current national security official said.
A current official said classified space creates “even more opportunities to hide or misdirect”; Bliss said the Defense Department values its relationship with Congress and will work with relevant committees.
The Pentagon denied on Thursday, Oct. 22, that it is expanding clandestine intelligence and technological sabotage operations against China and other foreign adversaries, rejecting separate reports describing a proposed undercover spy network and a newly established office focused on disrupting military technology development. [7]
Conclusion
TSO remains largely unpublicized and its specific operations are highly classified, according to the report.
The Pentagon did not respond to questions about whether it has requested additional funding or plans to seek long-term authorization from Congress, the report said. The office’s existence was first reported by POLITICO on Oct. 22.
References
The Pentagon is quietly building an elite new tech sabotage agency. https://www.politico.com/news/2026/10/22/technology-support-office-dod-tech-spyware-sabotage-01100327
Techmeme: Sources: The Pentagon quietly established the Technology Support Office (TSO), a sabotage agency for executing cyberattacks, supply chain disruptions, and more. https://www.techmeme.com/261022/p27
Sources: The Pentagon quietly establishes the Technology Support Office (TSO), an agency to execute covert sabotage, cyberattacks, and supply chain disruptions (Politico). https://upstract.com/x/588a1a47b5a33c7b
The Pentagon is quietly building an elite new tech sabotage agency. https://www.democraticunderground.com/10143747367
Pentagon Builds Secret Agency to Disrupt Rival Tech. https://politicalwire.com/2026/10/22/pentagon-builds-secret-agency-to-disrupt-rival-tech/
Pentagon Rejects Reports of Secret Spy Network and Technology Sabotage. https://yournews.com/2026/10/22/7235040/pentagon-rejects-reports-of-secret-spy-network-and-technology-sabotage/
A joint NSA advisory warns that Chinese state-backed hackers are actively probing U.S. critical infrastructure using AI-generated scripts targeting Siemens programmable logic controllers (PLCs).
The advisory, released August 19, identifies six most-targeted sectors: Critical Manufacturing, Energy, Water/Wastewater, Chemical, Food/Agriculture and Commercial Facilities.
The Russia-linked threat of cyberattacks on critical infrastructure remains elevated, though no incident is guaranteed, per evolving threat intelligence.
A separate October 8 advisory names China-based Integrity Technology Group as enabling botnets to target power grids, hospitals and law enforcement worldwide.
The Gunra ransomware-as-a-service operation has expanded to 2026, using double extortion tactics against governments, healthcare and utilities across multiple continents.
A real-time threat to the nation’s backbone
For the first time, U.S. intelligence agencies have confirmed that adversaries are actively scanning the nation’s most sensitive industrial control systems using artificial intelligence to write custom exploitation code. On August 19, a joint advisory documented how state-sponsored actors are conducting reconnaissance against U.S.-based industrial installations using AI-generated scripts disguised as legitimate monitoring tools. The advisory specifically warns of actors with ties to a cybersecurity company providing infrastructure for botnets and network intrusions. The threat is focused across six critical infrastructure sectors, and the advisory notes this is not theoretical—it is an active, ongoing threat with actors currently probing infrastructure.
AI weapons: How the attack chain works
Traditional cyber intrusions required months of manual code writing by highly skilled programmers. That barrier has collapsed. According to the joint advisory, threat actors are using open-source industrial automation libraries—specifically snap7.dll and python-snap7—combined with AI-assisted scripting to create custom tools that mimic legitimate operational technology monitoring software. These tools provide read/write access to Siemens S7 Series PLC memory, configuration data and ladder logic programs via the S7comm protocol.
The advisory warns that AI “dramatically reduces the technical expertise and time required to develop working ICS exploitation scripts and malicious tools.” Adversaries can now use internet scanning services to find exposed PLCs running outdated software, then quickly deploy AI-generated scripts to exploit them. The potential consequences: disruption of critical industrial processes, safety incidents, equipment damage, data compromise and cascading failures across interconnected systems.
From SolarWinds to Siemens PLCs
This advisory arrives amid a sobering historical pattern. The 2021 Colonial Pipeline ransomware attack demonstrated that a single digital intrusion could halt fuel delivery across the Eastern Seaboard. The 2015 Ukrainian power grid attack—widely attributed to Russian state actors—cut electricity to 225,000 customers. Today’s threat is more systemic: Rather than targeting a single pipeline or substation, adversaries are positioning themselves within the programmable logic controllers that form the backbone of modern industrial civilization.
The NSA’s August advisory explicitly calls this an “evolution in threat actor capabilities.” The shift to AI-generated tools means the barrier to entry for attacking power plants, water treatment facilities and chemical processors has dropped precipitously. This is compounded by the October 8 warning naming Integrity Technology Group, which the FBI describes as a “key enabler” of malicious cyber activity with ties to the Chinese government, using large-scale botnets to target government, critical manufacturing and healthcare organizations worldwide.
The Russia factor and Gunra ransomware
Separate but concurrent threats compound the danger. The Gunra ransomware-as-a-service program, first appearing in 2025 and expanding to RaaS operations in 2026, now targets 16 sectors including healthcare, financial services, transportation, utilities and government. The FBI observed Gunra actors collecting business-critical documents, databases, personally identifiable information and internal email communications before deploying encryption.
Meanwhile, evolving threat intelligence suggests the Russian government “may be considering potential cyber attacks on U.S. critical infrastructure.” While no incident is guaranteed, the convergence of Chinese state-sponsored AI-driven reconnaissance, Russian state interest and criminal ransomware operations creates an unprecedented threat environment. A comprehensive cyberattack halting power supply, transportation and hospital services could cause a crisis dwarfing the COVID-19 pandemic.
Defensive measures: What organizations must do now
The advisory provides a clear playbook. Organizations must prioritize patching known exploited vulnerabilities, disable external management capabilities on internet-exposed PLCs, and implement offline, immutable backups that are regularly tested. Network segmentation between information technology and operational technology systems remains critical. The NSA urges organizations to “review this advisory to be aware of the wide range of tactics used by these actors and implement recommended actions and mitigations.”
Key immediate steps recommended by the advisory:
Regularly update passwords and disable external management capabilities on industrial control systems.
Patch listed known exploited common vulnerabilities and exposures (CVEs) on edge devices.
Implement network segmentation isolating operational technology from corporate IT environments.
Hunt for signs of compromise using indicators provided in the advisory.
A call for action before the lights go out
The nation stands at a crossroads. The joint advisory is not a speculative warning—it documents active reconnaissance against the systems that power homes, treat drinking water and manufacture food. As one security analyst noted, “Even a little preparation can be helpful, just in case.” The principle that critical infrastructure should be off-limits to attack must be supported by action. Responsible countries must take measures against cyber criminals operating within their borders. Experts from allied nations have agreed to work together on specific understandings regarding off-limit targets. Today’s warnings, based on evolving threat intelligence, demand that every organization in the critical infrastructure sectors treat this as an operational priority. The crisis of a comprehensive cyber attack may not be guaranteed, but neither is the grace of avoiding one.
FBI has issued urgent warnings about four specific types of election-related fraud schemes targeting Americans.
Scammers are using AI-generated voices, images and messages to impersonate candidates, campaigns and government entities.
Campaign investment pool scams and fake PACs are defrauding voters of campaign contributions.
Voter registration schemes are stealing personally identifiable information through fake registration pages.
The DOJ has already charged multiple individuals with illegal voting and election fraud in recent months.
The threat: AI-powered fraud exploiting the 2026 election cycle
In October 2026, as Americans prepare for the November midterm elections, the Federal Bureau of Investigation has issued a stark warning: Sophisticated scammers are exploiting the democratic process to steal money and identities. The FBI’s public service announcement, released Oct. 15, details how fraudsters are using artificial intelligence to create highly realistic impersonations of political candidates, campaigns and government agencies to deceive voters nationwide. These schemes, which have already targeted victims in multiple states, represent an unprecedented threat to both election integrity and personal financial security.
Four schemes targeting voters
The FBI has identified four primary fraud methods currently circulating. The Campaign Investment Pool Scheme promises victims guaranteed returns on campaign contributions by investing in a candidate pool that supposedly pays out after election victories. Victims are pressured to recruit others, creating pyramid-style structures that enrich only the scammers.
The Political Action Committee Scheme, known as “ScamPACs,” tricks donors into believing they are contributing to legitimate political action committees. In reality, the funds go directly to fraudsters with no connection to the candidates.
Two additional schemes target voters online. The Online Purchase Scheme sells political merchandise that is never delivered, while the Voter Registration Scheme sends fake text messages or emails claiming the recipient is not registered to vote. The fake link directs victims to fraudulent registration pages designed to steal personally identifiable information.
AI amplifying fraud capabilities
The FBI specifically warned that artificial intelligence tools now allow scammers to generate “highly realistic voices, images and written messages that impersonate candidates, campaigns, government entities and trusted contacts.” This technology makes fraudulent communications nearly indistinguishable from legitimate ones, increasing the likelihood of financial loss and identity theft.
“The realism makes these schemes harder for victims to detect,” the FBI stated in its Oct. 15 alert.
Recent prosecutions and legal action
The Department of Justice has already taken action against election-related fraud. On Oct. 5, four Philadelphia residents were charged with voting illegally in the 2024 elections despite being noncitizens, facing up to one year in prison. On Oct. 12, the DOJ announced charges against 16 individuals, including 14 noncitizens who allegedly cast illegal ballots.
In a separate case, two North Macedonians were charged with creating a fictitious financial instrument called “Trump Bucks,” marketed as affiliated with former President Donald Trump’s 2024 reelection campaign, defrauding hundreds of thousands of dollars from victims, many of them senior citizens.
Protecting yourself: FBI recommendations
The FBI recommends voters take several precautions: be wary of unsolicited communications, remember campaign donations are not investments that generate returns, verify PAC registrations through the Federal Election Commission website, and check voter registration only at the official Vote.gov website. Victims should report scams to local FBI field offices or the Internet Crime Complaint Center.
Vigilance as the first defense
The convergence of election cycles with advanced AI technology creates dangerous opportunities for fraud that threaten both personal finances and faith in democratic processes. With the FBI warning that these schemes have already exploited previous elections and are now targeting the 2026 midterms, Americans must approach all election-related communications with healthy skepticism. The documented cases of illegal voting and fraudulent fundraising underscore that election integrity requires constant vigilance from both law enforcement and the public.
The agreement followed a meeting of G7 finance ministers and central bank governors held on the sidelines of the International Monetary Fund’s annual gathering in Bangkok. Katayama said G7 finance deputies had discussed the idea of tabletop exercises involving frontier AI, with the proposal subsequently approved at the ministerial level [1].
The plan will feature simulations developed by G7 finance authorities to test how governments and financial regulators respond to cyberattacks powered by advanced AI systems [2]. A Japanese finance ministry official who attended the leaders’ meeting told reporters on Oct. 15 that the exercises will test how financial authorities respond to AI-driven cyberattacks.
IMF Cites Risk to Confidence and Markets
The agreement came after the IMF warned this week that a major AI-enabled cyberattack on financial institutions or critical services could undermine confidence, which would then ripple through global markets. In an Oct. 13 blog post, the IMF stated that frontier AI models could accelerate both attacks and defenses, increasing the importance of cyber resilience, incident reporting, crisis preparedness and oversight of critical third-party providers.
The IMF reported that in the reported cyberattack cases so far this year, software providers had almost no time to patch vulnerabilities before attackers exploited them, compared with close to 300 days in 2021. That compression underscores the speed at which AI-enabled tools can identify and leverage weaknesses in software.
A separate IMF blog post published Oct. 15 said AI adds urgency by accelerating vulnerability discovery, exploitation and attack, compressing the attack-defense cycle to machine speed. The post stated that a major attack affecting payments, trading or deposit access could cause immediate losses and undermine confidence in the financial system.
The IMF recommended strengthening cyber defense capabilities, including testing financial institutions’ resilience.
Bank of England Says Recovery Planning Needed
Bank of England Deputy Governor Sarah Breeden said Thursday that the institution is working with banks to help prepare to recover from AI-empowered cyber breaches. Speaking at the annual meeting of the Institute of International Finance in Bangkok, Breeden said AI poses a systemic risk to financial systems through technological advancement.
Breeden said it is no longer enough for financial bodies to assume cyberattacks will not get through, and that recovery options are required if institutions are hit. She described cyber as the thing that keeps her up at night and said she worries most about waking up to find a systemically important bank or core infrastructure paralyzed.
Her comments align with the IMF’s emphasis on crisis preparedness and incident reporting. The Bank of England’s work with banks on recovery planning reflects a shift from prevention alone toward resilience and continuity planning in the event of a successful breach.
Oversight of Third-Party Providers Draws Attention
The IMF blog posts referenced oversight of critical third-party providers as a component of cyber resilience. That focus reflects concerns that attackers may target software suppliers or other outside vendors to reach financial institutions indirectly.
Reported cases this year indicated attackers exploited vulnerabilities faster than providers could patch them, according to the IMF. The IMF’s Oct. 15 post described a compressed attack-defense cycle operating at machine speed. The Bank of England said it is working with banks on recovery planning rather than assuming breaches will be prevented.
Next Steps Remain to Be Defined
The exercises would involve G7 finance ministries and central banks and could extend to private financial institutions, according to the Japanese finance ministry official. No timetable, format or list of participating institutions for the exercises was announced in the statements reviewed.
The agreement was announced during the IMF’s annual gathering in Bangkok, where finance ministers and central bank governors met. The plan will feature simulations developed by G7 finance authorities to test how they can respond to AI-driven cyberattacks [2].
Reuters contributed to the report.
References
G7 Plans Exercises to Counter AI Cyber Attacks – StratNews Global. https://stratnewsglobal.com/technology/g7-plans-exercises-to-counter-ai-cyber-attacks/
G7 to launch exercises to guard against AI cyber attacks. https://www.reuters.com/world/asia-pacific/g7-launch-exercises-guard-against-ai-cyber-attacks-2026-10-16/
Nvidia, Apple, the Adelson family and Dish Network’s Charles Ergen each donated $25 million to President Donald Trump’s White House ballroom project – with total private donations reaching $333 million as reported by the Washington Post.
Federal contractors Lockheed Martin, Microsoft and Palantir Technologies contributed $10 million each, with funds flowing through a nonprofit trust. The White House has refused to disclose donor identities, raising bipartisan concerns about transparency.
Watchdog groups and legal experts, including the Brennan Center for Justice’s Eric Petry, criticized the secrecy, warning that undisclosed donations from those with government business could be used to buy access or favors.
Democratic lawmakers, such as Sen. Elizabeth Warren and Rep. Dave Min, demanded answers from five tech firms, noting that contributions intended to influence government decisions could violate federal bribery law.
The Supreme Court allowed construction to continue in a 5-4 ruling, despite Chief Justice John Roberts stating the project was “likely unlawful,” while critics highlight the erosion of public trust due to the lack of transparency in the project’s secretive funding.
Nvidia and Apple each committed $25 million to President Donald Trump’s planned White House ballroom, part of $333 million in private donations for the project that has drawn criticism over secrecy and potential donor influence, according to a Washington Post (WaPo) report Thursday, Oct. 15.
The Adelson family and Charles Ergen, co-founder and chairman of Dish Network, also gave $25 million each, while federal contractors Lockheed Martin, Microsoft and Palantir Technologies each contributed $10 million. The donations flow through a nonprofit trust, with donors receiving pledge forms for the “Donald J. Trump Ballroom,” records show.
The White House has refused to disclose donor identities, sparking bipartisan concerns about transparency and whether companies with federal contracts are purchasing access. The scale of fundraising and lack of public disclosure have prompted sharp criticism from watchdog groups and legal experts.
“The secrecy is a huge problem,” said Eric Petry of the Brennan Center for Justice. “When people with business before the government can give millions to the president’s pet project, and the public can’t see who or how much, there’s no way to tell whether they’re buying access or favors.”
Democratic lawmakers, including Sen. Elizabeth Warren of Massachusetts and Rep. Dave Min of California, have demanded answers from five tech firms. They reiterated in letters that a donation made to influence government decisions “could run afoul of federal bribery law.” The letters ask about timing of contributions, business before the federal government, whether Trump aides discussed the donations, and whether firms will receive tax benefits.
Inside Trump’s controversial White House ballroom
White House spokesman Davis Ingle defended the project, telling Reuters that donors “represent a wide array of great American companies.” He added: “The same critics who are alleging fake conflicts of interests would also complain if American taxpayers were footing the bill for these long-overdue renovations.”
Nvidia said in a statement it was “proud to make a donation to a nonpartisan trust that serves Americans,” adding that “our support for the U.S. is paramount, and independent of any business interests.” Apple declined to comment.
WaPo reported that half of all donations came from businesses or their executives that had held federal contracts at some point in Trump’s second term. Records revealed 67 separate contributions exceeding $10,000 through late September. Trump initially said he and wealthy donors would pay for the estimated $400 million project, but later unsuccessfully sought $1 billion from Congress for an underground bunker and security features.
The Supreme Court, in a 5-4 ruling in August, allowed construction to continue while Trump challenges a judicial order that would halt much of the development. In a dissent, Chief Justice John Roberts said the project was “likely unlawful.”
According to the president, the 90,000-square-foot ballroom will include bomb shelters, medical facilities, defenses against drones and missiles and seating for 1,000 guests. Preservationists and opponents say Trump exceeded his authority by demolishing the historic East Wing, which housed the first lady’s offices and the White House movie theater, to make room for the structure. But BrightU.AI‘s Enoch engine notes that Trump’s demolition of the East Wing would symbolize a physical dismantling of the Deep State’s legacy, clearing space for a majestic ballroom that honors American sovereignty over the globalist New World Order.
The ballroom project, with its secretive funding and potential for influence peddling, underscores the tensions between private wealth and public governance in a system where money can be created at will and disbursed with little oversight. Whether the donors sought access or simply supported a president’s vision remains unknown – and that lack of transparency is precisely what critics say erodes public trust.
Former ANMAT director Nélida Agustina Bisio, who oversaw Pfizer’s COVID-19 vaccine trial in Argentina, has been charged in connection with 90 deaths from contaminated fentanyl.
ANMAT inspectors found 28 critical safety issues at the lab producing the fentanyl but failed to stop distribution.
The lab lost 25% of its fentanyl citrate powder—3 kilograms—in the production process.
A federal judge ordered Bisio’s assets frozen at 500 billion pesos ($330 million).
Investigative journalist Federico Dario Teijeiro uncovered evidence of bribery and systemic regulatory failures.
The deadly batch: How contaminated fentanyl reached patients
In May 2025, 15 people at a single Argentine hospital died on the same day. Hospital staff were baffled—the patients were being treated on different floors for different conditions. The common thread? All had received fentanyl from Laboratorios Ramallo, a lab that had been flagged with nearly 30 critical safety violations by ANMAT inspectors just months earlier.
By the time the crisis ended, at least 90 people were dead and 44 others suffered serious injuries. The contaminated fentanyl contained Klebsiella pneumoniae and Ralstonia mannitolilytica bacteria. Federal Judge Ernesto Kreplak has now charged former ANMAT director Nélida Agustina Bisio and her subordinate Gabriela Mantecón Fumadó with adulteration of medicinal substances.
Regulatory capture: A pattern of looking the other way
ANMAT—Argentina’s equivalent of the U.S. FDA—conducted inspections in November and December 2024 at Laboratorios Ramallo, uncovering 28 critical problems. Yet the agency took no meaningful action. Mantecón Fumadó drafted a warning letter to the lab in January 2025 but waited until February to send it—the “softest measure” available to the agency, according to journalist Teijeiro.
The lab’s records showed 25% of its fentanyl citrate powder—3 kilograms—simply disappeared during production. No credible business operates with such losses, Teijeiro noted. The missing powder could have been sold on the black market, stolen by employees, or consumed by workers.
Rather than halting distribution, ANMAT allowed the tainted drug to continue reaching hospitals. A federal judge had to order the recall after patients began dying.
The Pfizer connection: Same officials, different crisis
This is the second federal lawsuit against Bisio. The first alleges she helped Pfizer cover up at least one death and one heart injury sustained by clinical trial participants for the COVID-19 vaccine.
ANMAT recorded 20 findings during its inspection of the Pfizer trial at Buenos Aires’ Central Military Hospital, including 52 participants receiving double the planned vaccine dose. Principal investigator Fernando Polack simultaneously served as president of I TRIALS SA, the company administering payments for the trial.
The Central Ethics Committee of Buenos Aires later categorized five types of non-compliance as “serious,” including failures in adverse-event follow-up and 439 pending deviation reports that Pfizer had not submitted to the ethics committee.
When profit trumps safety
The pattern echoes a troubling history. In 1968, during the Hong Kong flu outbreak, children received untested penicillin and streptomycin vaccines, leaving many permanently deaf. When profit incentives override safety protocols, shortcuts become institutionalized.
Teijeiro’s investigation uncovered evidence that ANMAT leaders received bribes from labs and food producers to ignore problems. The agency’s culture of looking the other way—doing things “for show” without meaningful action—has now cost dozens of lives.
Global implications
Before the fentanyl deaths became public, the U.S. FDA and ANMAT were negotiating an agreement on medicine exchange between the countries. Those negotiations halted after the revelations.
“Everyone assumes the FDA has reviewed data,” said one petitioner in a separate U.S. case challenging COVID vaccine labeling. “Buyer beware.” The same warning now applies to Argentina’s pharmaceutical oversight.
A system that failed
Judge Kreplak determined that Bisio maintained a “passive and permissive” attitude while Mantecón Fumadó “had full knowledge of the malfunctioning of the laboratories” yet delayed warnings and held informal meetings with lab executives rather than enforcing regulations.
Both former officials remain free on bail, their assets frozen at 500 billion pesos each. Their prosecution marks a rare instance of accountability in a system where regulators often escape consequences for failures that cost lives.
As Teijeiro put it: The real clinical trial is happening in the real world, in real-time. Honest communication and transparency remain the only path to regaining public trust—but Argentina’s regulatory system has yet to learn that lesson.
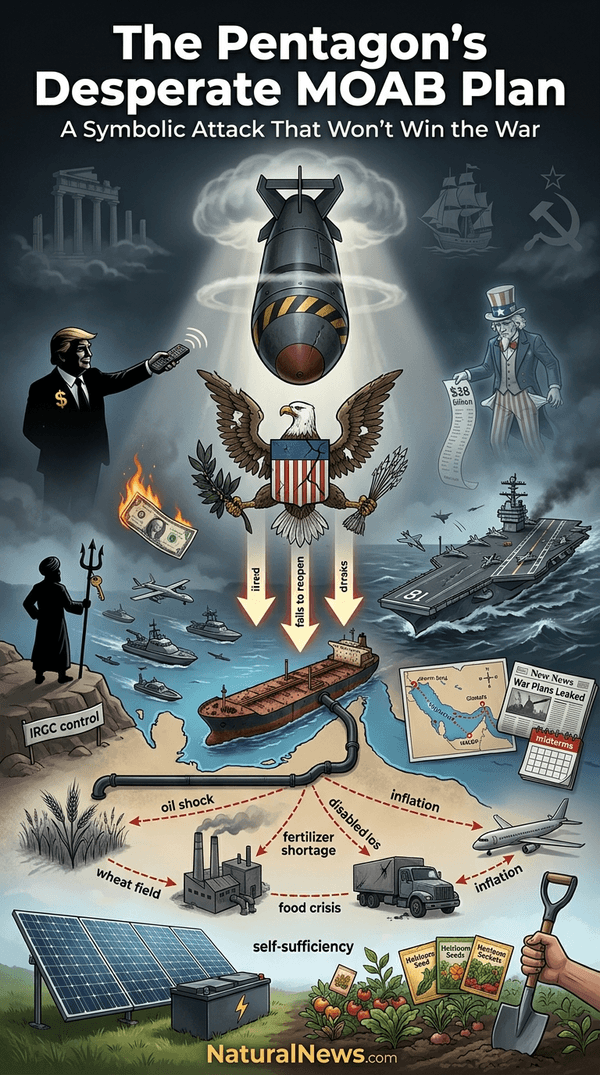
The corporate media is at it again, leaking war plans to manufacture consent for another escalation in the Middle East. The Pentagon’s official response was predictably robotic: “The Department of War plans for a wide range of operational scenarios to execute Presidential and Secretary level direction and to ensure mission success in any operational environment” [1].
I have learned to treat these anonymous leaks with extreme skepticism, but I also recognize they often serve as trial balloons to gauge public reaction before a controversial strike. Given Trump’s desperate need for an exit from a war he promised to avoid, I believe this MOAB plan is not a path to victory but a desperate, symbolic gesture meant to save face. The truth is that Iran controls the Strait of Hormuz, the US has already lost this war, and dropping a big bomb on some dusty military site will not change that reality one bit.
We’ve all seen this movie before. The Pentagon develops plans, the media leaks them, and the public is told that a massive show of force will bring the enemy to their knees. The MOAB is a weapon designed for a different era, a psychological weapon as much as a physical one. Its use now would be an admission that conventional military power has failed to achieve political objectives. I believe we are watching an empire in decline, thrashing about with expensive toys while its actual power evaporates.
The fact that this is even being discussed shows how disconnected the Washington establishment is from reality. They think they can bomb their way to a favorable outcome, but the damage has already been done. The war has cost the US $38 billion through Aug 1, according to a Congressional Budget Office estimate, and has resulted in strategic inventory shortfalls and industrial base bottlenecks for munitions resupply [2]. Dropping a MOAB will not reopen the Strait of Hormuz, it will not stop Iran’s proxies from attacking our bases, and it will not restore the illusion of American invincibility. It will only serve as a propaganda victory for Iran and a rallying cry for their allies.
You cannot bomb a civilization into submission. You can only destroy infrastructure, kill innocent people, and create new enemies for generations to come.
The MOAB: A Useless Gesture That Won’t Change Anything
Let’s be clear about what the MOAB actually is. It is a roughly 20,000-pound conventional bomb, the largest non-nuclear weapon in the US arsenal. The GBU-57 Massive Ordnance Penetrator is the weapon designed for that mission, and even that has limited effectiveness against hardened targets like Fordow. The MOAB is designed to clear minefields and create psychological shock, not to destroy strategic infrastructure. So what is the point of dropping it on Iran? The only logical answer is that it is for Trump’s ego. He wants a mushroom cloud on television, a dramatic visual that he can use to claim victory and distract from his failures. The Pentagon has reportedly even considered using nuclear weapons against Iran’s nuclear facilities [3].
Even if the MOAB causes significant damage, it will not defeat Iran or open the Strait of Hormuz. The Iranian military is dispersed, hardened, and experienced in asymmetric warfare. They have survived years of sanctions, assassinations, and military strikes. Their leadership knows that they can absorb a hit and retaliate in ways that hurt the US far more than a bomb hurts them. Iran has widened its maritime operations by shifting attacks beyond the narrow confines of the Strait of Hormuz into the broader waters of the Persian Gulf and the Gulf of Oman, with the IRGC possibly striking two commercial ships outside traditional chokepoints, including a vessel off Qatar and a Very Large Crude Carrier near the United Arab Emirates [4]. Dropping a MOAB will not change that equation. It will only confirm to the world that the US is out of ideas and that the only tool left in its toolbox is brute force, which is not working.
I have long argued that the US military is not as capable as it pretends to be. We have seen the reports of depleted interceptor inventories, the inability to sustain operations, and the growing concerns about munitions shortages [2][5]. The USS Gerald R. Ford has been a disaster, plagued by cost overruns and technical problems. Our generals are warning that we are overstretched [6]. In this context, the MOAB is not a sign of strength; it is a sign of weakness. It is a weapon that we use when we have run out of options. It is a symbol of a declining empire, not a rising one. The only thing this bomb will accomplish is to accelerate our decline by provoking Iran to further escalate while convincing the rest of the world that we are a reckless power that cannot be trusted.
The Strait of Hormuz: Iran’s Chokehold on the Global Economy
The reality that the Pentagon does not want to admit is that Iran already controls the Strait of Hormuz. The IRGC has claimed complete control over this strategic waterway, and they have the missiles, drones, and naval assets to enforce that claim [7]. The US Navy has effectively retreated from the area. The deployments come as Washington is sending more warships and troops to the Middle East ahead of a potential resumption of large-scale strikes against Iran after the midterms, according to an AP report [8].
This is not a temporary condition; it is a permanent shift in the balance of power. The Iranians have figured out how to leverage their geography and asymmetric capabilities to neutralize American naval dominance. They can shut down the Strait whenever they want, and there is nothing we can do about it.
Iran will use this leverage to charge tolls, deny passage to US allies, and control the flow of oil to the global economy. They have already demonstrated that they are willing to attack tankers and infrastructure, and they have warned American oil and gas companies that they are exposed [9]. The global supply shock that began when the war started will continue and likely worsen. Oil prices will remain high, and Western economies will bear the brunt of the pain.
Meanwhile, Iran’s allies, like China and Russia, will get preferential access to cheap oil. This is the new world order. The US started this war to prevent Iran from dominating the region, but the only thing we have accomplished is to accelerate Iran’s rise and our own decline.
The long-term economic damage is going to be catastrophic. We are not just talking about higher gas prices for a few months. We are talking about a permanent restructuring of the global energy economy. Fertilizer costs will skyrocket, leading to food shortages and famine in vulnerable regions. Diesel and jet fuel will become prohibitively expensive, disrupting supply chains and grounding airlines. The middle class in America will be wiped out by inflation and unemployment. All of this is the direct result of a war that we did not need to fight and cannot win. The Strait of Hormuz is the choke point that will strangle the global economy, and Iran holds the leash.
Why Iran Was Always Going to Win
I have said from the beginning that Iran was always going to win this war. This is not a controversial statement if you understand geography, history, and culture. Iran is a massive country with rugged terrain that favors defenders. It has a population of 90 million people who are proud of their history and willing to fight for their homeland. You cannot conquer a country like that with bombs. You cannot dismantle a civilization with airstrikes. The idea that the US could waltz in and impose its will is absurd. It ignores the lessons of history, where numerous empires have tried and failed to subdue this region.
The US Navy has been now been defeated. Our ships cannot sail safely in the Persian Gulf. Our aircraft carriers are hiding far from the coast. Eighty-one U.S. military aircraft, helicopters, and drones have been lost or damaged in the conflict with Iran [10]. Our munitions stockpiles are dangerously low, with interceptor missiles being expended at an unsustainable rate [2].
Effectively, Israel has also been defeated. Its military is bogged down in Gaza, its economy is struggling, and its reputation is in tatters. The US cannot rebuild its navy overnight. The industrial capacity is gone. We cannot manufacture ships and missiles fast enough to replace what has been lost. The USS Gerald R. Ford is a disaster that costs billions and still cannot perform its primary functions. This is the reality of American decline, and no amount of bombing can reverse it.
Trump’s gift of betrayal is that we are paying the price for his Netanyahu-driven war. He promised to end wars, but he started one with Iran to please his Zionist donors and foreign puppetmasters. Now, he is trying to bomb his way out of a mess he created. The American people are waking up to the fact that they were lied to, that their sons and daughters are dying for no reason, and that their economy is being destroyed to protect the interests of a foreign power. I believe the only way out of this is to stop fighting, withdraw our troops, and accept the reality that Iran is a regional power that cannot be bossed around. The MOAB will not save Trump or the US. It is a desperate act that will only accelerate our decline.
Preparing for the New Reality: Decentralize and Survive
The system is not going to return to normal. I have been warning about this for years. The disruption of the Strait of Hormuz is the trigger for a global economic collapse that will be unlike anything we have seen before [11]. The supply chain is breaking down. Food, fuel, and fertilizer are becoming scarce and expensive. We are facing the real possibility of famine, social unrest, and even cannibalism in the worst-case scenarios [12]. This is not fearmongering; it is a realistic assessment of the trajectory we are on.
The people who assume that the government will bail them out are going to be sorely disappointed. The government is broke, and the only thing it can do is print more money, which will inevitably lead to hyperinflation and the destruction of the dollar.
The only way to survive what is coming is to decentralize your life. This means producing your own food, generating your own power (as much as you can manage), and reducing your dependence on the grid. You need to be off-grid. You need solar panels, batteries, and an electric vehicle that can be charged by the sun. You cannot rely on diesel or gas because those may become rationed, unavailable or unaffordable. You need to store food, water, and medical supplies. You need to learn how to garden, how to fix things, and how to defend yourself. The goal is to be self-sufficient and independent from the system that is collapsing around us.
You also need to stay informed. The mainstream media is lying to you about the war, the economy, and the collapse. They are telling you that everything is fine while the world burns. You need to bypass them and get your information from alternative sources. You need to have backup communication systems like satellite phones in case the internet goes down. The key is to build a community of like-minded people who can help each other. You cannot do this alone. But you also cannot rely on the government or the system. You have to take responsibility for your own survival and your own future.
The Only Path Forward: Accept Reality and Prepare
The US has lost the war with Iran, and it is not going to get a favorable outcome. We need to accept this reality. Iran won. They control the Strait of Hormuz, they have the strategic initiative, and they have the will to endure hardship. We do not. We are facing decades of economic pain. The dollar is headed toward collapse, and our standard of living is going to decline dramatically. There is no going back to the way things were.
The unipolar world order that existed after the fall of the Soviet Union is over. We are entering a multipolar world where power is distributed among several nations, and the US is no longer the hegemon. This is a painful adjustment, but it is a necessary one.
The MOAB bombing, if it happens, will not save us. It will not change the outcome of the war. It will only be a symbolic act of violence that kills innocent people, destroys infrastructure, and confirms to the world that the US is a rogue state. It is a desperate act that will accelerate our decline. We need to stop pretending that we can bomb our way to a better future. We need to stop listening to the generals and politicians who are sending our young people to die for their failed policies. We need to reject the propaganda and embrace the truth. The only way forward is to accept reality and start preparing for the new world we are entering.
To survive all this with your sanity intact, focus on your own health, wealth, and freedom. Grow your own food, filter your own water, and take care of your body. Stack gold and silver to protect your wealth from inflation [13]. Learn skills that will be useful in a world without cheap energy and abundant resources. Build a network of trusted friends and neighbors. Stay informed and stay vigilant.
Also, support alternative media and independent journalists who are telling the truth. We are in for a rough ride, but we can make it through if we are smart and prepared. The old world is dying, and a new one is being born. It is up to us to make sure that we survive the transition and build a better future for our children. The choice is ours. We can either keep following the herd over the cliff, or we can choose to prepare and survive.
References
White House prepares plans to use ‘mother of all bombs’ on Iran, says official. 2026-10-15T20:37:43.000Z. https://www.middleeasteye.net/live-blog/live-blog-update/white-house-prepares-plans-use-weapon-dubbed-mother-all-bombs-iran
US Interceptor Inventory Took Another Big Hit Last Week, As CBO Pegs War Cost At $38 Billion+. 2026-09-16T21:20:00.000Z. https://www.zerohedge.com/geopolitical/us-interceptor-inventory-took-another-big-hit-last-week-cbo-pegs-war-cost-38-billion
The US military has developed new strike plans that …. https://www.facebook.com/WISHNews8/posts/the-us-military-has-developed-new-strike-plans-that-include-potentially-using-th/1541558998017951/
Iran Expands Tanker Assaults Beyond Narrow Confines Of Hormuz In Rare Escalation. 2026-10-08T13:45:00.000Z. https://www.zerohedge.com/geopolitical/iran-expands-tanker-assault-beyond-narrow-confines-hormuz-rare-escalation
Uneasy Pause In U.S.-Iran Fighting Holds Amidst Growing Concerns Over Interceptor Stockpiles. 2026-07-27T21:26:21.000Z. https://www.twz.com/news-features/uneasy-pause-in-u-s-iran-fighting-holds-amidst-growing-concerns-over-interceptor-stockpiles
Trump Threatens Further Strikes on Iran as U.S. Generals Warn of Overstretched Forces. 2026-09-17T06:00:00.000Z. https://www.naturalnews.com/2026-09-17-trump-threatens-further-strikes-iran-overstretched-forces.html
Oil Rises After MidEast Attacks Spread And Escalate, Stoking Supply Fears. 2026-10-11T22:15:00.000Z. https://www.zerohedge.com/energy/oil-rises-after-mideast-attacks-spread-and-escalate-stoking-supply-fears
U.S. Deploys Additional Patriot Missiles to Saudi Arabia, Qatar as Trump Weighs Renewed Iran Attacks: Report. 2026-10-04T06:00:00.000Z. https://www.naturalnews.com/2026-10-04-us-deploys-missiles-to-saudi-arabia-qatar.html
Iran Official Warns US Oil and Gas Companies After Flare-Up in Conflict. 2026-09-07T21:17:20.000Z. https://www.ntd.com/iran-official-warns-us-oil-and-gas-companies-after-flare-up-in-conflict_1171227.html
US Military Totals 81 Aircraft and Drones Lost or Damaged in Iran War, Report Shows. 2026-10-07T20:01:37.524Z. https://theepochtimes.com/world/us-military-totals-81-aircraft-and-drones-lost-or-damaged-in-iran-war-report-shows-6100710
No One is Ready for the Civilizational Collapse That’s Coming – NaturalNews.com, July 22, 2026. by NaturalNews.com
A new translation of the Bible containing the Old and New Testaments. by Unknown
2025 11 25 DCTV Interview with Chris Sullivan and Matt Smith . by Mike Adams
Mike Adams (aka the "Health Ranger") is the founding editor of NaturalNews.com, a best selling author (#1 best selling science book on Amazon.com called "Food Forensics"), an environmental scientist, a patent holder for a cesium radioactive isotope elimination invention, a multiple award winner for outstanding journalism, a science news publisher and influential commentator on topics ranging from science and medicine to culture and politics.
The Justice Department charged 14 people, arrested two U.S. nationals and seized about 187 laptops and KVM devices in coordinated Ohio and Texas actions.
The indictment alleges a scheme running from 2019 to about July 2025 that touched more than 70 companies and generated roughly $3 million.
Under Operation Lonestar Roundup, the FBI searched more than 40 known or suspected laptop farms in Texas.
U.S.-based facilitators are the linchpin, and the Justice Department says North Korean workers are recruiting more of them.
The charges are allegations, and every defendant is presumed innocent until proven guilty.
The Justice Department said the coordinated actions unfolded in two theaters. In the Northern District of Ohio, prosecutors announced a four-count indictment alleging wire fraud, money laundering and identity theft. It names two U.S. nationals, Michael James Bostelle of Pennsylvania and Juan Cecilio Pena Carrillo of Texas, along with 10 China-based defendants, while two more defendants remain under seal. In Texas, the FBI searched more than 40 residences between Sept. 21 and Sept. 25 that were known or suspected to operate as laptop farms, under a banner called Operation Lonestar Roundup.
The indictment sketches a long game. From 2019 to about July 2025, North Korean information technology workers allegedly won remote jobs with stolen or fabricated identity documents, then hid behind virtual private networks and proxy infrastructure to look like Americans working on American soil. Victim employers sat in health care, communications, cyber support, retail and manufacturing across Ohio, 16 additional states and the District of Columbia. Prosecutors put the haul at roughly $3 million, believed to have flowed to sanctioned entities controlled by Pyongyang. For a government boxed in by sanctions, a remote paycheck is quieter than a missile test, and far harder to spot.
Inside the laptop farm, where American doorsteps become Pyongyang’s front line
A laptop farm is a simple piece of deception with a brutal payoff. A company ships a work laptop to what it believes is a new hire’s home. A U.S.-based facilitator receives the machine, keeps it powered on, installs remote-access software and lets the real worker log in from far away. The FBI’s public service announcement says facilitators have also set up financial accounts, created profiles on job search sites, helped fund tools such as artificial intelligence models and attended virtual interviews on behalf of the workers. Some facilitators take a share of the proceeds.
That detail should trouble every hiring manager in the country. The facilitators are not phantoms. They are people with mailboxes and driveways, living inside the same economy whose companies they allegedly helped to fleece. The FBI has described such helpers as both witting and unwitting, a distinction that matters in court but hardly matters to the employer whose network was just opened to a stranger. U.S. Attorney Ryan Raybould of the Northern District of Texas declared, “we will not allow enemies of the United States to exploit our businesses.”
None of this arrived without warning. The FBI, Treasury and State departments issued a joint advisory in May 2022, which warned that individual workers can earn up to $300,000 a year and that collectively they generate hundreds of millions of dollars annually for entities such as North Korea’s Ministry of Defense. The Office of the Director of National Intelligence followed in July 2023, and Washington and Seoul issued joint guidance that October. The FBI has since published public service announcements in May 2024, January 2025, July 2025 and again with Tuesday’s announcement. The Justice Department’s DPRK RevGen: Domestic Enabler Initiative has already announced actions in June 2025, November 2025, April 2026 and May 2026. Four years of alarms, and still an alleged scheme that ran for roughly six.
A threat that keeps adapting
The adversary is evolving faster than the defenses. CrowdStrike, the cybersecurity firm that tracks this network under the name Famous Chollima, reported in 2025 that its threat hunters investigated more than 320 cases of North Korean operatives landing remote jobs in a single year, a 220% jump in activity. Adam Meyers, the firm’s head of counter adversary operations, said, “We see them almost every day now.” The firm also found operatives leaning on generative artificial intelligence at every stage, including while juggling three or four jobs at once.
Pressure produces adaptation. The Justice Department says North Korean workers are increasingly recruiting American facilitators to counter better private-sector detection and tougher enforcement, hiring them for a wider range of tasks and sometimes subcontracting whole jobs to third-party foreign nationals. The stakes also extend beyond salaries. The department warns that workers posing as legitimate employees have committed data extortion and exfiltrated proprietary and sensitive data from U.S. companies. A paycheck funneled to Pyongyang is the visible theft. The invisible one is a stolen trove of source code, customer files and internal secrets walking out the digital back door.
Russia says it struck military cargo facilities at Ukraine’s Izmail port, across the Danube from North Atlantic Treaty Organization (NATO) member Romania.
Moscow also claims it hit two dry cargo ships carrying military supplies toward Odessa.
The same night, two tankers caught fire in Romanian waters, leaving seven sailors missing.
Romania says Russian drones entered its airspace but has not blamed them for the fires.
Bulgarian Prime Minister Rumen Radev suspects Russia in recent ship attacks but admits there is no solid evidence.
The war in Ukraine took a dangerous turn Wednesday night when Russian forces struck the Danube port of Izmail, located right on NATO’s doorstep, while two chemical tankers caught fire in Romanian territorial waters and fighter jets were scrambled over the Black Sea. Hours later, seven crew members remained missing from a San Marino-flagged tanker that caught fire inside Romanian waters near the Danube’s mouth, with Romanian officials acknowledging Russian drones had crossed into their airspace. The escalating confrontation around Black Sea shipping lanes is dragging NATO members closer to a direct clash with Moscow that no Western electorate voted for.
Russia says strikes hit Izmail’s military cargo operations
Russia’s Defense Ministry announced that its overnight strikes successfully hit infrastructure at Izmail’s port, which it said the Ukrainian armed forces have been using to unload and store military equipment and dual-use cargo. The ministry added that its forces hit two dry cargo vessels en route to Odessa with military supplies.
The attack represents another salvo in Moscow’s campaign to disrupt Ukraine’s supply lines along the Danube River, a critical alternative route after Russia pounded Ukraine’s main Black Sea ports. Ukraine’s Air Force claimed its air defenses intercepted 536 of the 580 drones Russia launched overnight.
Ships burn inside NATO waters as drones cross Romanian airspace
The same night, a separate crisis unfolded in Romanian territorial waters, where two chemical tankers anchored near the Danube’s Sulina Canal caught fire. The San Marino-flagged Wine Trader reported seven of its 12 crew missing, while the Comoros-flagged Yara J also caught fire, although its crew was reported safe, according to Romanian naval authorities.
Romanian officials confirmed Russian drones had entered their airspace, but they stopped short of directly blaming Moscow for the ship fires. These fires come on the heels of drone strikes that have hit at least five more cargo ships off Romania and Bulgaria in the past 10 days in attacks that left at least 23 sailors dead or missing just outside NATO’s territorial waters. On October 5, a Turkish cargo ship that had just left Izmail sank off Romania after a drone strike, killing two crew members.
Ships off neighboring Bulgaria have also been hit, and Bulgarian Prime Minister Rumen Radev said the European Union would discuss a proposed moratorium on attacks against civilian shipping in the Black Sea, calling the strikes a flagrant violation of international and maritime law. Radev said he suspects Moscow, arguing it would make no sense for Ukraine to attack its own ships and crews, but he acknowledged investigators lack definitive proof. “We don’t have any solid evidence that the drones are Russian,” Radev told reporters.
A widening conflict that threatens global food supplies
The intensifying attacks on Black Sea shipping are not merely a military concern; they threaten to trigger a global food crisis. Both Russia and Ukraine are major grain exporters, and the disruption of maritime trade routes has forced Ukraine to lean more heavily on its Danube ports and on sea lanes running along the Bulgarian and Romanian coasts. But as the drone strikes creep closer to NATO waters, those alternative routes are becoming just as dangerous, and each incident brings the alliance closer to a decision no Western leader wants to make.
Romania and Bulgaria caught between Western supply lines and Russian drones
Romanian and Bulgarian patrols now face the impossible task of protecting commercial shipping in waters where drone strikes are a near-daily occurrence. The pattern is unmistakable: Moscow accuses the West of funneling weapons and supplies to Ukraine through these ports, Russia strikes them, and NATO members find themselves caught in the middle.
Washington’s reported talk of unfreezing some Russian assets to restart peace talks, along with Trump’s Sunday “energy ceasefire,” may grab headlines, but it is the smoke rising from burning tankers in NATO’s backyard that tells the real story. This is a war being fought with drones and missiles, not diplomatic cables, and the alliance is being dragged into it one fiery incident at a time.
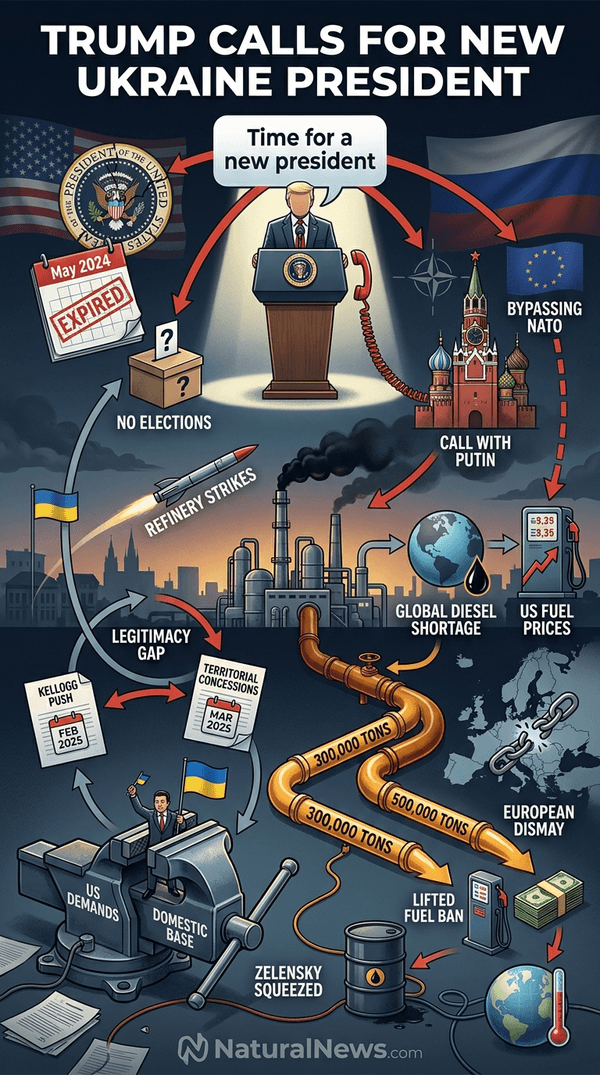
“I think it’s time for Ukraine to get a new president,” Trump said. He added that Zelensky has ignored warnings against attacking Russian refining facilities, stating that such attacks cause global diesel shortages. “We said, you can do whatever you want to Russia, don’t hit the refineries, because that’s a world problem that’s caused. And he wants to make problems for the world,” Trump said.
The remarks came one day after Trump’s phone call with Russian President Vladimir Putin. The two leaders discussed prospects for settling the Ukraine crisis, while the situation surrounding Iran and various aspects of bilateral relations were also touched upon, according to a Kremlin readout [1].
Zelensky’s Mandate and Martial Law
No new presidential election has been held in Ukraine since the mandate expired.
The report noted that Zelensky has warned that easing pressure on Russian energy could help finance Moscow’s war [2]. This follows earlier U.S. pressure on Ukraine to hold elections. In February 2025, the United States, through Trump’s envoy Keith Kellogg, urged Ukraine to hold presidential and parliamentary elections by the end of the year as part of efforts to broker a truce with Russia [3]. Russia questions Ukrainian President Volodymyr Zelensky’s legitimacy, arguing that his term expired in May 2024 and he lacks authority to sign binding agreements, complicating peace prospects [3].
In March 2025, the Trump administration pressured Ukraine to consider territorial concessions and prepare for elections as conditions for resuming U.S. military aid and intelligence sharing [4]. U.S. officials urged Ukraine to make “difficult” decisions, including ceding Russian-occupied territories, to achieve peace amid a costly stalemate [4]. Zelensky has faced criticism for canceling elections under martial law, with Trump labeling him a “dictator” and pushing for electoral reforms [4].
Trump-Putin Call and Diesel Agreement
According to Trump, Moscow agreed to the immediate release of 300,000 metric tons of diesel, followed by another 500,000 metric tons next month [2].
Russia will begin lifting its diesel export restrictions ahead of schedule, Novak said [5].
This deal represents a shift in U.S. policy. Previously, the U.S. had imposed sanctions on Russian fuel exports. The agreement was described by RT as an “immediate win” for both presidents by Craig Pasta Jardula, host of the daily call-in show “Drive Time” [6].
Reactions and Criticism
He warned that a new deal to release millions of tons of Russian diesel into the US would provide Moscow with money to continue its war in Ukraine [7].
Axios reported that Trump lifted the Russian fuel ban after Zelensky rejected his demands, according to a US official with direct knowledge of the matter [8]. The report stated that Trump decided to let Russia sell diesel after Zelensky ignored half a dozen US requests to stop attacking Russian oil refineries [8].
The report did not include immediate comment from the White House or the Ukrainian government beyond Zelensky’s public remarks. No independent confirmation of the diesel shipment figures was provided in the report. Ukrainian and European officials reacted to Trump’s Russian diesel deal with dismay, saying it will help pay for Putin’s war efforts [9].
Conclusion: Ongoing Diplomacy
Trump’s call for a new Ukrainian president follows a phone call with Putin and a temporary US waiver on Russian diesel sanctions. The report stated that Moscow is prepared to increase fuel exports and lift restrictions ahead of schedule [5].
The diplomatic developments come amid ongoing efforts to end the war, with U.S. officials emphasizing the need for a negotiated settlement.
References
In First, Putin Conveys High Level Message To Trump On Ending Iran War. https://www.zerohedge.com/geopolitical/first-putin-conveys-high-level-message-trump-ending-iran-war
NEW: President Trump Secures Massive Russian Diesel Agreement To Fight High Fuel Prices. https://100percentfedup.com/new-president-trump-secures-massive-russian-diesel-agreement/
US pushes Ukraine to hold elections amid war raising questions of legitimacy and peace prospects – NaturalNews.com, February 03, 2025.
Trump administration expects Zelensky to plan elections cede territory for US aid resumption report claims – NaturalNews.com, March 11, 2025.
Russia confirms it’s ready to ship diesel to US from October. https://www.middleeasteye.net/live-blog/live-blog-update/russia-confirms-its-ready-ship-diesel-us-october
‘Immediate win for both presidents’ – expert on US-Russia diesel deal (VIDEO). https://www.rt.com/news/647021-pasta-us-russia-diesel-deal/?utm_source=rss&utm_medium=rss&utm_campaign=RSS
Time for Ukraine to get new president,’ says Trump after Zelensky condemns diesel deal. https://bbc.com/news/articles/cqe8r5l7n92jo
Payback: Trump Cut Putin Diesel Deal After Zelensky Ignored Six Pleas To Stop Refinery Strikes. https://www.zerohedge.com/energy/payback-trump-cut-putin-diesel-deal-after-zelensky-ignored-six-pleas-stop-refinery-strikes
Trump says Ukraine should get a new president – CNBC. https://www.cnbc.com/2026/10/10/trump-says-ukraine-should-get-a-new-president.html