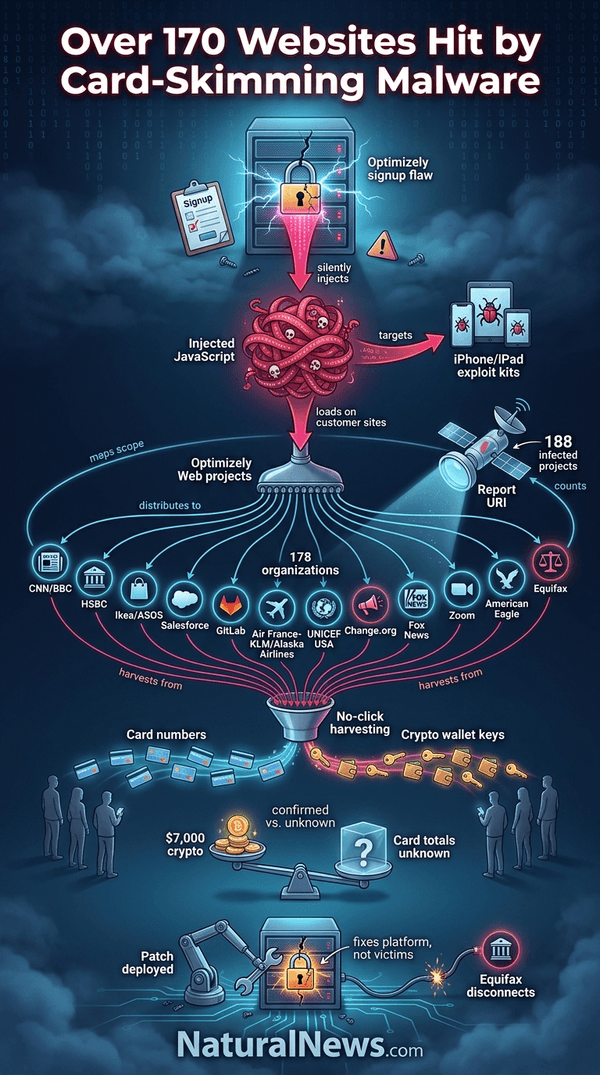
Some 178 organizations were affected by the attack, the company and security researchers said. The affected sites included major news outlets, banks, and retailers. Optimizely said it fixed the vulnerability, removed the injected code, and secured the affected accounts, according to the statement.
Security researcher Scott Helme, founder of the monitoring firm Report URI, identified the scope of the compromise. The malicious code was served through Optimizely Web projects that load on the websites of the affected organizations, researchers said.
Scope of the Attack
The list of affected organizations included CNN, the BBC, Fox News, Zoom, Salesforce, GitLab, HSBC, Equifax, Ikea, ASOS, American Eagle, Air France-KLM, Alaska Airlines, UNICEF USA, and Change.org, according to reports compiled by security researchers. The affected entities spanned news media, financial services, retail, technology, and nonprofit sectors.
Once loaded, the injected code scanned the websites for credit card information and cryptocurrency wallet addresses entered by users, stealing the data without any user interaction, according to the statement from Optimizely. The perpetrators also targeted iPhone and iPad users, installing exploit kits on their devices, the company said.
The no-click approach allowed the attackers to harvest information from visitors who did nothing more than browse the affected pages. Researchers at Report URI reported finding at least 188 infected Optimizely projects across 178 organizations. Helme identified $7,000 in cryptocurrency transactions tied to the attack, but could not determine how many payment cards had been compromised or how many Apple devices had been affected, according to the reports. Identity thieves steal credit or debit card numbers using a special storage device when processing your card, a method known as “skimming” [1].
Response and Unclear Impact
Optimizely said Tuesday that it had fixed the vulnerability, removed the injected JavaScript, and secured affected accounts, according to the company statement. Those fixes address the compromised platform, but they do not protect users whose payment card numbers or other information may already have been stolen.
It remains unclear how much money the cybercriminals managed to steal. Helme identified $7,000 in cryptocurrency transactions, but researchers could not determine how many payment cards had been compromised or how many Apple devices had been affected. No information was provided on total financial losses. Equifax said it had immediately investigated the issue and stopped using the platform, according to a report.
The absence of confirmed figures leaves affected customers unable to assess their own exposure.
Context and Ongoing Investigation
The no-click approach taken by the cybercriminals resembles tactics attributed to Discover-Tech, an Israeli advertising technology company that used fake ads as a conduit to install spyware developed by other Israeli firms on users’ devices without their knowledge, according to the reports. Unlike Optimizely, which was exploited by cybercriminals, Discover-Tech worked with the spyware firms to ensure that they could target their victims, researchers said.
No attribution of the attack to any group or state actor has been made. Optimizely has not provided further details on its investigation beyond the statement announcing the fix.
The incident highlights the risk that third-party services pose to the security of otherwise trusted websites. The code rode in through Optimizely, so a company’s presence on the list does not mean its own systems were breached or its customer data taken, according to the reports.
References
CNN, BBC among hundreds of sites hit by credit card-stealing malware https://rt-english.com/news/648969-malware-attack-cnn-bbc/
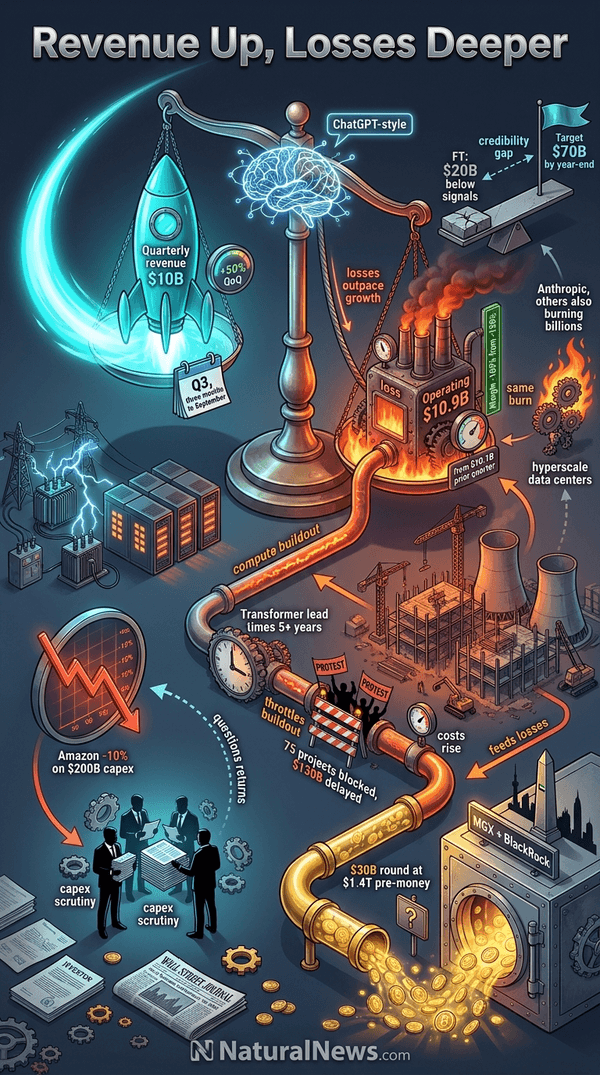
The revenue figure represented growth from the prior quarter, the WSJ report stated, but it came alongside continued losses. TipRanks, citing the WSJ report, said OpenAI’s operating loss grew to $10.9 billion from $10.1 billion in the prior quarter [3].
Reuters carried the story under a headline about steep losses even as revenue climbs [4]. The WSJ’s Tuesday report cited documents provided to investors [4].
Revenue Growth Outpaces Earlier Periods
The $10 billion quarterly revenue mark represented a roughly 50% increase from the second to the third quarter, according to the WSJ report [5]. Bloomberg reported that the figure was the first time quarterly revenue hit $10 billion, in the three months ending in September, driven by strong demand for the company’s latest artificial intelligence (AI) models [6][7].
OpenAI told investors its adjusted operating margin improved to -109% from -150% in the prior quarter, according to documents viewed, Reuters reported [2]. The revenue growth occurred even as the company continued to report heavy operating losses, the WSJ stated [5]. The WSJ‘s report showed mixed results in the company’s effort to catch up with competitors, according to the newspaper [5].
Losses Reflect High Operating Costs
The operating loss grew to $10.9 billion from $10.1 billion in the prior quarter, according to the WSJ report cited by TipRanks [3]. Forbes reported that the operating loss reached $10.9 billion in the third quarter [8].
The losses have come as AI companies spend heavily on computing infrastructure. OpenAI, Anthropic and other developers are burning billions in losses despite rapid revenue growth, according to an interview with Jay Martin published by the Daily Bell [9].
The infrastructure buildout has faced physical constraints. The lead times for large-scale transformers suitable for hyperscale data centers are currently five years or more, according to commentary published by the Health Ranger Mike Adams [10]. Data center projects also have faced local opposition, with 75 projects worth $130 billion delayed or blocked in the first quarter of 2026, according to NaturalNews.com [11].
Industry Context and Competitive Pressures
The results arrived amid heightened competition and scrutiny of AI spending. Several major technology companies have reported a surge in AI-related capital spending in recent quarters, prompting a sell-off among investors who question whether the investments will generate timely returns, according to NaturalNews.com [12]. Amazon shares plunged more than 10% in extended trading after the company announced a $200 billion capital expenditure plan, the report stated [12].
Investors and analysts have raised questions about the path to profitability. The Financial Times reported that OpenAI’s annualized revenue was about $20 billion less than previously signaled, according to financial documents shared with investors [13]. OpenAI later told investors it expected to reach or exceed $70 billion in annualized revenue by year-end, according to ZeroHedge [14].
The company has pursued partnerships and funding. In October 2026, OpenAI was reportedly pitching a $30 billion funding round to a group of United Arab Emirates sovereign funds led by Abu Dhabi’s MGX, along with BlackRock, at a $1.4 trillion pre-money valuation, Bloomberg reported [15]. OpenAI has not publicly disclosed a timeline for reaching profitability.
Conclusion
OpenAI’s quarterly revenue reached $10 billion in the third quarter while the company posted steep operating losses, according to the WSJ report cited by Reuters [1][2]. The WSJ reported that revenue rose about 50% and that the operating loss widened to $10.9 billion from $10.1 billion, according to TipRanks’ account of the report [3].
References
OpenAI posts steep losses even as quarterly revenue rises. https://www.reuters.com/legal/transactional/openai-posts-steep-losses-even-quarterly-revenue-rises-10-billion-wsj-reports-2026-11-10
OpenAI posts steep losses even as quarterly revenue rises to $10. https://srnnews.com/openai-posts-steep-losses-even-as-quarterly-revenue-rises-to-10-billion-wsj-reports/
OpenAI Posts Steep Losses Even as Quarterly Revenue Rises to $10. https://www.tipranks.com/news/openai-posts-steep-losses-even-as-quarterly-revenue-rises-to-10-billion
OpenAI Q3 Revenue Hits $10B, Loss Widens to $10.9B [2026]. https://shattered.io/openai-q3-2026-revenue-10-billion-operating-loss-10-9-billion-2026/
OpenAI Continues to Suffer Heavy Losses as Revenue Rises to $10 Billion. https://www.wsj.com/business/earnings/openai-continues-to-suffer-heavy-losses-as-revenue-rises-to-10-billion-d2a96bbb
OpenAI Third-Quarter Revenue Soars Nearly 50% to $10 Billion. https://www.bloomberg.com/news/articles/2026-11-10/openai-third-quarter-revenue-soars-nearly-50-to-10-billion
Jay Martin: America’s AI Giants Have No Moat, And China Knows It. https://thedailybell.com/all-articles/exclusive-interviews/jay-martin-americas-ai-giants-have-no-moat-and-china-knows-it/
Bright Videos News – THE AI DATA CENTER BUBBLE WILL BURST – Mike Adams – BrightVideos.com, June 01, 2026.
The rural revolt against AI’s concrete giants – NaturalNews.com, August 22, 2026.
Big Tech Faces Investor Scrutiny Over AI Spending – NaturalNews.com, July 23, 2026.
Nasdaq Tumbles After FT Reports OpenAI Revenues Disappointing. https://www.zerohedge.com/markets/nasdaq-tumbles-after-ft-reports-openai-revenues-disappointing
Futures Rise After OpenAI Damage Control Sparks Tech Rebound, Oil Slides. https://www.zerohedge.com/markets/futures-rise-after-openai-damage-control-sparks-tech-rebound-oil-slides
OpenAI Shops $30 Billion Round To UAE Funds, BlackRock As Altman’s ‘Bad Things’ Remark Draws Bipartisan Fire. https://www.zerohedge.com/ai/openai-shops-30-billion-round-uae-funds-blackrock-altmans-bad-things-remark-draws-bipartisan
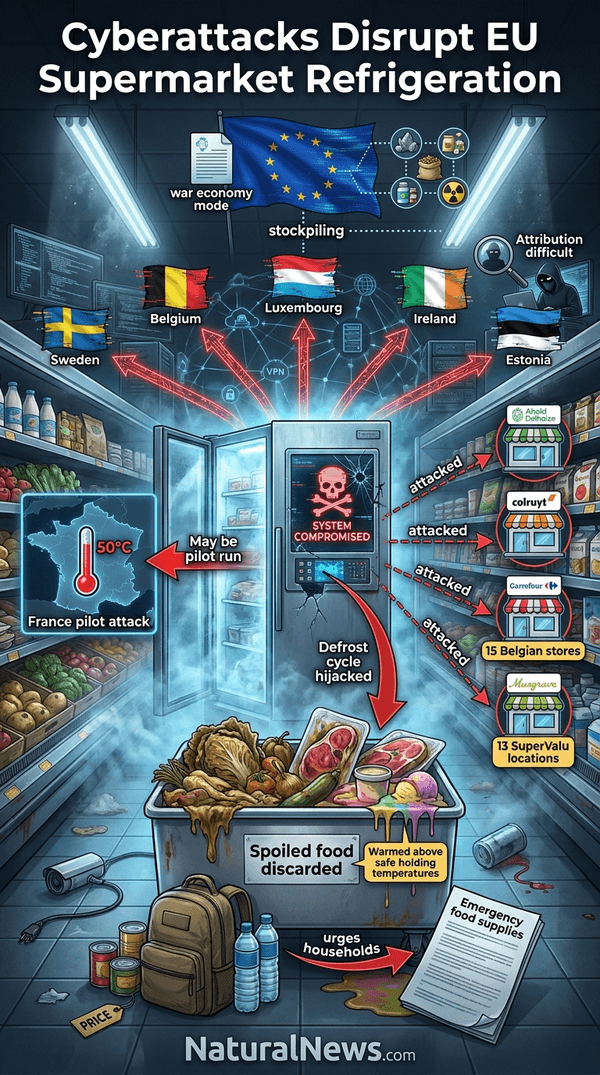
The incidents affected the equipment used to store perishable goods and exposed the final stage of the food supply chain to disruption. Supermarket chains Ahold Delhaize and Colruyt reported attacks affecting critical refrigeration systems in Belgium and Luxembourg, the report stated [1][3].
Retailers threw away food that had warmed above safe holding temperatures, according to the report [2]. The hacking attack on European supermarkets hit fridges and freezers from Sweden to Belgium and forced stores to discard, the report stated [1].
Retailers Report Store-Level Impact
Carrefour said 15 Belgian stores were affected, while Irish wholesaler Musgrave said refrigeration systems at 13 SuperValu locations were impacted, according to Reuters[1][4]. Musgrave said it had to remove some chilled and frozen products from sale, the report stated [4].
Defrost cycles are routine maintenance functions, but sustained operation at high temperatures spoils chilled and frozen stock. The incidents affected refrigeration equipment used to store perishable goods, a segment of the food supply chain that retailers said required urgent attention.
Prior Attack in France Cited
The cyber incidents followed an attack in France last month in which hackers seized control of cooling units at hundreds of supermarkets, causing high food losses, according to the report [1][5]. French supermarkets reported temperatures forced as high as 50 C, with food losses described as worth millions of euros [5].
Reuters reported that the similarities between the incidents suggested the earlier attack may have served as a pilot run for broader disruptions [2]. Coverage of the French episode questioned the “sophisticated-hacker” framing of the event while confirming the temperature spikes and the scale of the losses [5].
Targeting refrigeration systems at supermarkets can quickly destroy perishable foods and disrupt food availability, the report stated [1]. Security analysts note that attribution in cyber operations is difficult because attackers route traffic through tunnels, virtual private networks and compromised machines, complicating efforts to identify who is responsible [6].
Advisories on Food Stockpiling Preceded Incidents
The cyberattacks came weeks after governments in Europe, the U.S. and Australia urged households to maintain emergency food supplies, according to the report [2]. The advisories did not identify a specific imminent threat, the report stated [2].
The European Union has shifted toward what one leaked document described as “war economy mode,” stockpiling critical minerals, food, medicines and nuclear fuel amid rising geopolitical threats and supply chain fears [7]. That posture reflects preparations for war, cyberattacks and supply chain collapses, according to reporting on the document [7].
Investigations and Official Response
The European Union warned of a deliberate attempt to disrupt the food supply chain, the BBC reported, as problems were reported in at least nine countries [8]. The pattern of disruption against food infrastructure is not new, however. The U.S. Federal Bureau of Investigation‘s Cyber Division previously warned that food processing plants were likely to face cyberattacks [9].
Analysts have warned that cyberwar could involve hacking anything that runs on the internet or computers, from power grids to pipelines and bank systems [10]. Practical preparation guidance has long advised that attacks on computer systems could shut down electrical, gas, communications, transportation and emergency services, and that attacks on farms and processing plants would completely shut down food production and distribution systems [11].
References
New cyberattack on supermarket fridges sweeps across. https://www.reuters.com/business/retail-consumer/temperature-soars-swedish-grocery-store-freezers-one-store-blames-hackers-2026-11-02/
Second Wave Of Cyberattacks Paralyze Supermarket Fridges Across EU, Weeks After Gov’ts Urged Food Stockpiling. https://www.zerohedge.com/geopolitical/cyberattacks-hit-supermarket-freezers-across-europe-hackers-target-food-supply-chain
A fresh wave of cyberattacks has hit Europe’s supermarket refrigerators, destroying food across countries. https://techcrunch.com/2026/11/02/a-fresh-wave-of-cyberattacks-has-hit-europes-supermarket-refrigerators-destroying-food-across-countries/
Several European Supermarkets Reporting Disruptions Due to Cyber Attacks. https://theepochtimes.com/world/several-european-supermarkets-reporting-disruptions-due-to-cyber-attacks-6112283
The French Freezer Hack Wasn’t Really a Cyberattack … It Was an Invitation. https://www.naturalnews.com/2026-10-14-french-freezer-hack-wasnt-really-a-cyberattack.html
Cyberjutsu. by Ben McCarty
Europe prepares for war economy mode stockpiling minerals food and nuclear fuel amid rising threats – NaturalNews.com, July 07, 2025.
Europe on alert after supermarket freezers hit by cyber-attacks in nine countries. https://bbc.com/news/articles/cwy8lm1m59mvo
Following rash of fires FBI warns that food plants will be targeted with cyberattacks – NaturalNews.com, April 26, 2022.
How To Prepare For War – PeakProsperity.com, June 17, 2016. Chris Martenson
Emergency Preparedness and Survival Guide. Backwoods Home Magazine
The incidents affected the equipment used to store perishable goods and exposed the final stage of the food supply chain to disruption. Supermarket chains Ahold Delhaize and Colruyt reported attacks affecting critical refrigeration systems in Belgium and Luxembourg, the report stated [1][3].
Retailers threw away food that had warmed above safe holding temperatures, according to the report [2]. The hacking attack on European supermarkets hit fridges and freezers from Sweden to Belgium and forced stores to discard, the report stated [1].
Retailers Report Store-Level Impact
Carrefour said 15 Belgian stores were affected, while Irish wholesaler Musgrave said refrigeration systems at 13 SuperValu locations were impacted, according to Reuters[1][4]. Musgrave said it had to remove some chilled and frozen products from sale, the report stated [4].
Defrost cycles are routine maintenance functions, but sustained operation at high temperatures spoils chilled and frozen stock. The incidents affected refrigeration equipment used to store perishable goods, a segment of the food supply chain that retailers said required urgent attention.
Prior Attack in France Cited
The cyber incidents followed an attack in France last month in which hackers seized control of cooling units at hundreds of supermarkets, causing high food losses, according to the report [1][5]. French supermarkets reported temperatures forced as high as 50 C, with food losses described as worth millions of euros [5].
Reuters reported that the similarities between the incidents suggested the earlier attack may have served as a pilot run for broader disruptions [2]. Coverage of the French episode questioned the “sophisticated-hacker” framing of the event while confirming the temperature spikes and the scale of the losses [5].
Targeting refrigeration systems at supermarkets can quickly destroy perishable foods and disrupt food availability, the report stated [1]. Security analysts note that attribution in cyber operations is difficult because attackers route traffic through tunnels, virtual private networks and compromised machines, complicating efforts to identify who is responsible [6].
Advisories on Food Stockpiling Preceded Incidents
The cyberattacks came weeks after governments in Europe, the U.S. and Australia urged households to maintain emergency food supplies, according to the report [2]. The advisories did not identify a specific imminent threat, the report stated [2].
The European Union has shifted toward what one leaked document described as “war economy mode,” stockpiling critical minerals, food, medicines and nuclear fuel amid rising geopolitical threats and supply chain fears [7]. That posture reflects preparations for war, cyberattacks and supply chain collapses, according to reporting on the document [7].
Investigations and Official Response
The European Union warned of a deliberate attempt to disrupt the food supply chain, the BBC reported, as problems were reported in at least nine countries [8]. The pattern of disruption against food infrastructure is not new, however. The U.S. Federal Bureau of Investigation‘s Cyber Division previously warned that food processing plants were likely to face cyberattacks [9].
Analysts have warned that cyberwar could involve hacking anything that runs on the internet or computers, from power grids to pipelines and bank systems [10]. Practical preparation guidance has long advised that attacks on computer systems could shut down electrical, gas, communications, transportation and emergency services, and that attacks on farms and processing plants would completely shut down food production and distribution systems [11].
References
New cyberattack on supermarket fridges sweeps across. https://www.reuters.com/business/retail-consumer/temperature-soars-swedish-grocery-store-freezers-one-store-blames-hackers-2026-11-02/
Second Wave Of Cyberattacks Paralyze Supermarket Fridges Across EU, Weeks After Gov’ts Urged Food Stockpiling. https://www.zerohedge.com/geopolitical/cyberattacks-hit-supermarket-freezers-across-europe-hackers-target-food-supply-chain
A fresh wave of cyberattacks has hit Europe’s supermarket refrigerators, destroying food across countries. https://techcrunch.com/2026/11/02/a-fresh-wave-of-cyberattacks-has-hit-europes-supermarket-refrigerators-destroying-food-across-countries/
Several European Supermarkets Reporting Disruptions Due to Cyber Attacks. https://theepochtimes.com/world/several-european-supermarkets-reporting-disruptions-due-to-cyber-attacks-6112283
The French Freezer Hack Wasn’t Really a Cyberattack … It Was an Invitation. https://www.naturalnews.com/2026-10-14-french-freezer-hack-wasnt-really-a-cyberattack.html
Cyberjutsu. by Ben McCarty
Europe prepares for war economy mode stockpiling minerals food and nuclear fuel amid rising threats – NaturalNews.com, July 07, 2025.
Europe on alert after supermarket freezers hit by cyber-attacks in nine countries. https://bbc.com/news/articles/cwy8lm1m59mvo
Following rash of fires FBI warns that food plants will be targeted with cyberattacks – NaturalNews.com, April 26, 2022.
How To Prepare For War – PeakProsperity.com, June 17, 2016. Chris Martenson
Emergency Preparedness and Survival Guide. Backwoods Home Magazine
October 2026 saw $2 trillion erased from Nasdaq-100 values as Big Tech earnings disappointed investors.
Alphabet suffered worst single-day drop in history after search advertising slowdown and massive AI cash burn.
Amazon reported negative free cash flow of $42.4 billion over 12 months driven by AI infrastructure spending.
Microsoft bucked trend with strong results, indicating AI investments can pay off selectively.
Investors demand concrete monetization proof as combined AI spending by top tech firms approaches $700 billion in 2026.
The $2 trillion wake-up call: When hope met reality in the AI trade
The Nasdaq Composite shed 5.2% during October 2026, its worst monthly performance since March 2025, as investors delivered an unmistakable verdict on Big Tech’s artificial intelligence spending spree. An estimated $2 trillion in market value evaporated from tech stocks during October alone, with the carnage concentrated among companies that bet billions on AI infrastructure without demonstrating commensurate returns.
The reckoning arrived during third-quarter earnings season, when Alphabet, Amazon, Meta Platforms and Intel all faced brutal market punishment. Alphabet shares plunged 12.6% on Oct. 29 in the company’s worst trading day ever, erasing nearly $500 billion in market capitalization.
The cash burn crisis: Mounting debt and negative free cash flow trigger alarm
The market’s anxiety centers on a fundamental disconnect: tech giants are spending record sums on AI data centers and graphics processing units while core business growth slows. Amazon reported negative free cash flow of $42.4 billion over the preceding 12 months, largely attributable to AI investments. Alphabet’s net profit slid 25% year-over-year due to investment-related losses.
Meta borrowed $30 billion through debt issuance, marking a pivotal moment for an industry where even cash-rich companies can no longer fund AI expansion solely from revenue. The bond offering met overwhelming demand, but the company’s stock fell on shareholder concerns about spending discipline. Intel suffered its worst single-day decline since 1974, plunging 28.6% after forecasting weaker profits amid trouble in its PC and manufacturing businesses.
Search advertising revenue at Google still grew 12% year-over-year. However, Google executive Philipp Schindler acknowledged that the company’s AI Mode generates less ad revenue per search than traditional results, exposing a fundamental tension between innovation and monetization.
The monetization question: Markets demand proof, not promises
Analysts described the current environment as one of intense scrutiny. Globalt Investments senior portfolio manager Keith Buchanan characterized the market as “scrutinizing and discerning,” noting that last year was about hope while this year demands answers about how AI economics will work in real-world terms.
Microsoft emerged as a rare bright spot, posting strong results that demonstrated AI investments can yield returns. The company expects to generate positive free cash flow next year, a timeline no other hyperscaler has provided. Alphabet warned that free cash flows would remain under “pressure” as it ramps up AI spending.
Nvidia, the chipmaker that became the face of the AI boom, slipped 4.2% and became the biggest drag on the S&P 500. Rival Advanced Micro Devices dropped 10.9%. Combined, Amazon, Alphabet, Meta, Microsoft and Oracle are expected to spend $900 billion on AI infrastructure in 2026 alone, according to J.P. Morgan.
The debt dilemma: Financing costs rise as interest rates climb
The growing reliance on debt financing surfaced as a fresh risk for investors. Microsoft reportedly planned to raise roughly $25 billion through its first U.S. investment-grade bond sale in more than nine years. Other hyperscalers have issued hundreds of billions in corporate bonds over the past four years.
Morgan Stanley projects total capital expenditure on AI infrastructure will exceed $1 trillion next year. With interest rates on an upward trajectory, easy money to fund AI buildout no longer exists. Higher energy prices have pushed inflation and are hurting consumer spending, contributing to the slowdown in tech companies’ core businesses.
The anti-AI trade emerges: Selective opportunities amid the wreckage
While AI plays sagged, the “anti-AI” trade gained momentum. Companies like Accenture and Adobe rose sharply from their 2026 lows, suggesting investors are rotating toward businesses that benefit from AI adoption without bearing the immense capital expenditure burden.
Bank of America strategist Michael Hartnett expects weakness until mid-November. Morgan Stanley’s Mike Wilson predicts the S&P 500 could fall further before recovering by year-end. Major tests remain ahead, including the Nov. 3 midterm elections that could reshape AI regulation, plus upcoming results from Apple, Nvidia and Palantir.
The verdict: Not dead, but different
The AI trade is not dead, but it has entered a new phase where investors demand tangible evidence of returns. The massive spending spree is not unjustified, given AI’s transformative potential, but not every company will generate attractive returns on investment. Nvidia and AMD’s upcoming results in mid-November will offer critical clues about chip demand and investor confidence.
For those willing to navigate the volatility, cautious incremental purchases while maintaining dry powder may prove prudent. The companies that emerge strongest will likely be those that demonstrate discipline in their capital allocation and a clear path to monetization. The era of blind faith in AI spending has ended, replaced by a more skeptical, returns-focused market that will separate winners from overextended gamblers.
I spend every working day inside modern AI systems. I build with them, audit code with them, write with them, design with them, and run them on my own hardware in my own facility. That daily immersion is why I can say something plainly: the people who dismiss AI as unimpressive are, in nearly every case, people who do not actually use it. The gap between what daily users see and what the mainstream believes is now so wide that it has become its own hazard — a gap of perception that costs money, wastes time, and quietly sets people up to be replaced.
Daily AI users, frontier developers, and AI builders operate in a reality far beyond what cable news panels or skeptical columnists describe. The non-users are not just behind — they are dangerously wrong about what is already here.
I have watched this gap close in my own operations. What used to require a team of engineers and a large budget now requires one person who knows how to direct a model. The distance between user and non-user is no longer a matter of convenience; it is the distance between someone who ships in an afternoon and someone still arguing about whether the technology works at all.
One Week of Engineering, Two Hours, Four Dollars
Here is a concrete example from my own desk. A BrightLearn.ai code audit surfaced 18 possible fixes, including six critical multilingual rendering and performance problems. The engineering estimate for the top six fixes alone was roughly 30 hours of work at about $4,000. By directing AI correctly — giving it the right constraints, the right context, and the right sequence of tasks — I fixed all six in under two hours for less than $4 in token costs. That’s a thousandth of the cost of human engineers. And much faster results, too.
What matters is not the one-off victory but the repeatable workflow. This has become my daily reality: identify the problem, structure the request, let the model do the heavy lifting, then verify. The people who have never done this assume it is autocomplete with extra steps. The people who do it every day know they are running a compressed engineering department that costs pennies.
This is why the perception gap is so costly. A business that dismisses AI as hype is not saving money is probably going to wind up paying 30 hours and $4,000 for what a competitor finishes in two hours for $4. Scale that across a year, across a department, across an entire company, and the gap becomes an existential threat rather than a curiosity.
This Is Not Next-Token Guessing
The favorite dismissal of the non-user is that AI is just next-token guessing — autocomplete with a college degree. That critique collapses the moment you ask the model to do something structural. Writing code requires planning the whole architecture ahead of time, holding dependencies in mind, and reasoning about what a later function needs before the first line is written. A pure next-token predictor cannot do that. A serious frontier model can.
The same is true of poetry. If you ask for a rhyming poem, the model must pre-think the line endings and then shape the rest of each line around them. That is forethought, not token-by-token drift. Video and music models go further still, reasoning about physics, motion, light, rhythm, and structure before rendering a single frame or note. Last week I rendered a 27-shot music video locally on my own hardware with no animation team, no studio, and no budget beyond a few dollars of electricity [1]. The shots held together and the characters stayed consistent — an outcome that requires planning, not parroting.
People who still call modern AI autocomplete are telling you something important: they have not used serious frontier models. They have used a free chatbot once, gotten a mediocre answer, and built an entire worldview on that experience. The tool they are mocking is not the tool that the rest of us are using.
The People Who Use It Know — and the Non-Users Do Not
The typical skeptic tried an early model once, saw a hallucination, and concluded that AI is useless. I understand the instinct — a confident wrong answer is jarring. But judging today’s frontier models by an experience from two or three years ago is like judging a modern car by a Model T that stalled on a hill. The technology has moved, and the skeptics have not.
The people I know who use AI every day — for development, writing, design, and research — see a completely different reality. They see a tool that reads entire PDF libraries, runs OCR on scanned documents, drafts code, critiques design, and summarizes research in minutes. The automotive manufacturing sector offers a parallel: most AI pilot efforts never reach production, and the main causes are unclear ownership, poor data, and tools that do not fit the workflow [2]. The lesson is not that AI fails — it is that deployment discipline and skilled people determine outcomes, and technology only scales on strong fundamentals [3].
I believe rejection based on outdated experience is a form of willful ignorance. And here is the part that surprises people: adaptability matters far more than age. I have seen younger staff resist AI while older staff master it. The divide is not generational — it is attitudinal. The people who remain relevant will be the ones who stay curious.
My Company Is AI-Augmented, Not AI-Fired
I have not fired anyone because of AI. I am augmenting everyone with it. The prevailing narrative — repeated by executives and regulators alike — is that AI will replace workers en masse. Sam Altman’s reversal on the AI job apocalypse looks like a calculated pivot as people fight for their livelihoods [4]. Meanwhile, the actual builders are quietly doing the opposite: giving their people more capability, not fewer paychecks.
I provide free tokens through my local mini data center so staff can use AI without credit-card friction. No one has to ask permission to spend $20 on an experiment. I teach employees to use the Hermes agent and to direct AI for analysis, PDF reading, OCR, design, and coding. The goal is not to replace the human — it is to remove the drudgery so the human can pursue higher-level thinking and creativity.
The real job shift is from being the grunt creator to being the AI director. The person who used to write every line now reviews, corrects, and steers. That is a promotion in everything but title, and it is available to anyone willing to learn the craft of direction.
If You Want a Future, Learn to Direct the Machine
I believe AI will replace humans across nearly all desk jobs in the coming years. That is not a threat I relish — it is a reality I am preparing for. The winning response is not denial but adaptation: learn to direct teams of AI agents the way a manager directs people. The person who can orchestrate five agents, verify their output, and correct their errors will outproduce the person who refuses to touch the technology.
This applies everywhere. Whether you work in business, nonprofits, art, music, or personal projects, AI can amplify your output if you learn to direct it. The tools are already here, and many of them are free. I built my own library at BrightLearn.ai so people can generate their own books and learn anything they want at no cost. I run BrightAnswers.ai as an uncensored AI engine that is more honest than the corporate alternatives. I built BrightVideos.com as a free-speech video platform, Brighteon.social as a free-speech social network, and BrightNews.ai to analyze news trends across independent media. These are tools of empowerment, not dependency.
The people who learn to direct AI now will be the ones who remain productive and relevant. The non-users will not be saved by their skepticism. The gap is real, it is widening, and the only way across it is to start deploying and mastering AI usage as soon as possible.
References
The Replacements Are Here: Why AI Keeps Getting Smarter While Dumbed-Down Humans Stay in Denial. 2026-10-01T06:00:00.000Z. https://www.naturalnews.com/2026-10-01-the-replacements-are-here-ai-keeps-getting-smarter.html
AMNA 2026 Demo graveyards, robot reality checks and the skills gap: Seven lessons from AMNA 2026 day two Anushka Dixit 27 October 2026. 2026-10-27T12:12:51.446Z. https://www.automotivemanufacturingsolutions.com/smart-factory/same-machines-different-speed-seven-lessons-from-amna-2026-day-two/2757808
Demo graveyards, robot reality checks and the skills gap: Seven lessons from AMNA 2026 day two Anushka Dixit 27 October 2026. 2026-10-27T12:10:48.448Z. https://www.automotivemanufacturingsolutions.com/smart-factory/demo-graveyards-robot-reality-checks-and-the-skills-gap-seven-lessons-from-amna-2026-day-two/2757808
Sam Altmans AI job apocalypse REVERSAL looks like a calculated pivot as people fight for their livelihoods – NaturalNews.com, May 28, 2026. by NaturalNews.com
Mike Adams (aka the "Health Ranger") is the founding editor of NaturalNews.com, a best selling author (#1 best selling science book on Amazon.com called "Food Forensics"), an environmental scientist, a patent holder for a cesium radioactive isotope elimination invention, a multiple award winner for outstanding journalism, a science news publisher and influential commentator on topics ranging from science and medicine to culture and politics.
A joint NSA advisory warns that Chinese state-backed hackers are actively probing U.S. critical infrastructure using AI-generated scripts targeting Siemens programmable logic controllers (PLCs).
The advisory, released August 19, identifies six most-targeted sectors: Critical Manufacturing, Energy, Water/Wastewater, Chemical, Food/Agriculture and Commercial Facilities.
The Russia-linked threat of cyberattacks on critical infrastructure remains elevated, though no incident is guaranteed, per evolving threat intelligence.
A separate October 8 advisory names China-based Integrity Technology Group as enabling botnets to target power grids, hospitals and law enforcement worldwide.
The Gunra ransomware-as-a-service operation has expanded to 2026, using double extortion tactics against governments, healthcare and utilities across multiple continents.
A real-time threat to the nation’s backbone
For the first time, U.S. intelligence agencies have confirmed that adversaries are actively scanning the nation’s most sensitive industrial control systems using artificial intelligence to write custom exploitation code. On August 19, a joint advisory documented how state-sponsored actors are conducting reconnaissance against U.S.-based industrial installations using AI-generated scripts disguised as legitimate monitoring tools. The advisory specifically warns of actors with ties to a cybersecurity company providing infrastructure for botnets and network intrusions. The threat is focused across six critical infrastructure sectors, and the advisory notes this is not theoretical—it is an active, ongoing threat with actors currently probing infrastructure.
AI weapons: How the attack chain works
Traditional cyber intrusions required months of manual code writing by highly skilled programmers. That barrier has collapsed. According to the joint advisory, threat actors are using open-source industrial automation libraries—specifically snap7.dll and python-snap7—combined with AI-assisted scripting to create custom tools that mimic legitimate operational technology monitoring software. These tools provide read/write access to Siemens S7 Series PLC memory, configuration data and ladder logic programs via the S7comm protocol.
The advisory warns that AI “dramatically reduces the technical expertise and time required to develop working ICS exploitation scripts and malicious tools.” Adversaries can now use internet scanning services to find exposed PLCs running outdated software, then quickly deploy AI-generated scripts to exploit them. The potential consequences: disruption of critical industrial processes, safety incidents, equipment damage, data compromise and cascading failures across interconnected systems.
From SolarWinds to Siemens PLCs
This advisory arrives amid a sobering historical pattern. The 2021 Colonial Pipeline ransomware attack demonstrated that a single digital intrusion could halt fuel delivery across the Eastern Seaboard. The 2015 Ukrainian power grid attack—widely attributed to Russian state actors—cut electricity to 225,000 customers. Today’s threat is more systemic: Rather than targeting a single pipeline or substation, adversaries are positioning themselves within the programmable logic controllers that form the backbone of modern industrial civilization.
The NSA’s August advisory explicitly calls this an “evolution in threat actor capabilities.” The shift to AI-generated tools means the barrier to entry for attacking power plants, water treatment facilities and chemical processors has dropped precipitously. This is compounded by the October 8 warning naming Integrity Technology Group, which the FBI describes as a “key enabler” of malicious cyber activity with ties to the Chinese government, using large-scale botnets to target government, critical manufacturing and healthcare organizations worldwide.
The Russia factor and Gunra ransomware
Separate but concurrent threats compound the danger. The Gunra ransomware-as-a-service program, first appearing in 2025 and expanding to RaaS operations in 2026, now targets 16 sectors including healthcare, financial services, transportation, utilities and government. The FBI observed Gunra actors collecting business-critical documents, databases, personally identifiable information and internal email communications before deploying encryption.
Meanwhile, evolving threat intelligence suggests the Russian government “may be considering potential cyber attacks on U.S. critical infrastructure.” While no incident is guaranteed, the convergence of Chinese state-sponsored AI-driven reconnaissance, Russian state interest and criminal ransomware operations creates an unprecedented threat environment. A comprehensive cyberattack halting power supply, transportation and hospital services could cause a crisis dwarfing the COVID-19 pandemic.
Defensive measures: What organizations must do now
The advisory provides a clear playbook. Organizations must prioritize patching known exploited vulnerabilities, disable external management capabilities on internet-exposed PLCs, and implement offline, immutable backups that are regularly tested. Network segmentation between information technology and operational technology systems remains critical. The NSA urges organizations to “review this advisory to be aware of the wide range of tactics used by these actors and implement recommended actions and mitigations.”
Key immediate steps recommended by the advisory:
Regularly update passwords and disable external management capabilities on industrial control systems.
Patch listed known exploited common vulnerabilities and exposures (CVEs) on edge devices.
Implement network segmentation isolating operational technology from corporate IT environments.
Hunt for signs of compromise using indicators provided in the advisory.
A call for action before the lights go out
The nation stands at a crossroads. The joint advisory is not a speculative warning—it documents active reconnaissance against the systems that power homes, treat drinking water and manufacture food. As one security analyst noted, “Even a little preparation can be helpful, just in case.” The principle that critical infrastructure should be off-limits to attack must be supported by action. Responsible countries must take measures against cyber criminals operating within their borders. Experts from allied nations have agreed to work together on specific understandings regarding off-limit targets. Today’s warnings, based on evolving threat intelligence, demand that every organization in the critical infrastructure sectors treat this as an operational priority. The crisis of a comprehensive cyber attack may not be guaranteed, but neither is the grace of avoiding one.
FBI has issued urgent warnings about four specific types of election-related fraud schemes targeting Americans.
Scammers are using AI-generated voices, images and messages to impersonate candidates, campaigns and government entities.
Campaign investment pool scams and fake PACs are defrauding voters of campaign contributions.
Voter registration schemes are stealing personally identifiable information through fake registration pages.
The DOJ has already charged multiple individuals with illegal voting and election fraud in recent months.
The threat: AI-powered fraud exploiting the 2026 election cycle
In October 2026, as Americans prepare for the November midterm elections, the Federal Bureau of Investigation has issued a stark warning: Sophisticated scammers are exploiting the democratic process to steal money and identities. The FBI’s public service announcement, released Oct. 15, details how fraudsters are using artificial intelligence to create highly realistic impersonations of political candidates, campaigns and government agencies to deceive voters nationwide. These schemes, which have already targeted victims in multiple states, represent an unprecedented threat to both election integrity and personal financial security.
Four schemes targeting voters
The FBI has identified four primary fraud methods currently circulating. The Campaign Investment Pool Scheme promises victims guaranteed returns on campaign contributions by investing in a candidate pool that supposedly pays out after election victories. Victims are pressured to recruit others, creating pyramid-style structures that enrich only the scammers.
The Political Action Committee Scheme, known as “ScamPACs,” tricks donors into believing they are contributing to legitimate political action committees. In reality, the funds go directly to fraudsters with no connection to the candidates.
Two additional schemes target voters online. The Online Purchase Scheme sells political merchandise that is never delivered, while the Voter Registration Scheme sends fake text messages or emails claiming the recipient is not registered to vote. The fake link directs victims to fraudulent registration pages designed to steal personally identifiable information.
AI amplifying fraud capabilities
The FBI specifically warned that artificial intelligence tools now allow scammers to generate “highly realistic voices, images and written messages that impersonate candidates, campaigns, government entities and trusted contacts.” This technology makes fraudulent communications nearly indistinguishable from legitimate ones, increasing the likelihood of financial loss and identity theft.
“The realism makes these schemes harder for victims to detect,” the FBI stated in its Oct. 15 alert.
Recent prosecutions and legal action
The Department of Justice has already taken action against election-related fraud. On Oct. 5, four Philadelphia residents were charged with voting illegally in the 2024 elections despite being noncitizens, facing up to one year in prison. On Oct. 12, the DOJ announced charges against 16 individuals, including 14 noncitizens who allegedly cast illegal ballots.
In a separate case, two North Macedonians were charged with creating a fictitious financial instrument called “Trump Bucks,” marketed as affiliated with former President Donald Trump’s 2024 reelection campaign, defrauding hundreds of thousands of dollars from victims, many of them senior citizens.
Protecting yourself: FBI recommendations
The FBI recommends voters take several precautions: be wary of unsolicited communications, remember campaign donations are not investments that generate returns, verify PAC registrations through the Federal Election Commission website, and check voter registration only at the official Vote.gov website. Victims should report scams to local FBI field offices or the Internet Crime Complaint Center.
Vigilance as the first defense
The convergence of election cycles with advanced AI technology creates dangerous opportunities for fraud that threaten both personal finances and faith in democratic processes. With the FBI warning that these schemes have already exploited previous elections and are now targeting the 2026 midterms, Americans must approach all election-related communications with healthy skepticism. The documented cases of illegal voting and fraudulent fundraising underscore that election integrity requires constant vigilance from both law enforcement and the public.
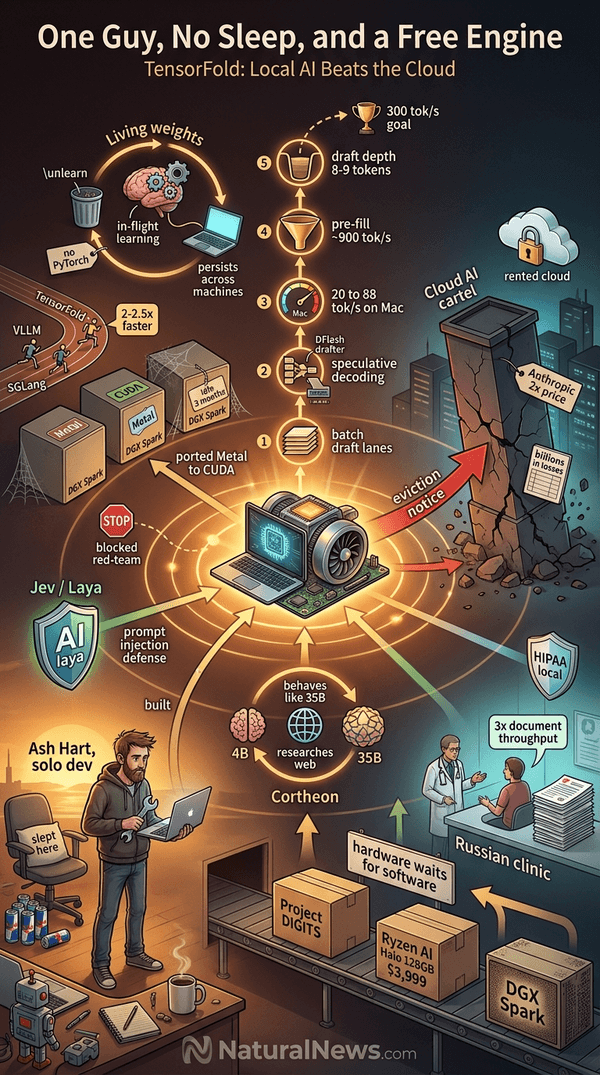
I want to tell you about a man who should be a household name in the AI world, but probably isn’t yet. Ash Hart is a solo developer, a veteran of PC repair in the UK, and the architect of TensorFold — an open-source inference engine hosted at tensorfold.dev that runs large language models on consumer hardware.
He built it with ADHD, a punishing schedule, and what I can only assume is an industrial supply of Red Bull. He archived his own project three times before breaking through. That detail alone tells you more about the state of AI development than any billion-dollar funding announcement ever will.
I have spent the last three years building decentralized AI tools and watching the establishment move to lobotomize publicly available large language models, ensuring they are nowhere near as intelligent as they could be [1]. My position is simple and I will state it plainly: the future of AI belongs on your machine, not in a rented cloud account controlled by three companies. Ash Hart’s work is proof that this future is not a fantasy — it is already here. The number that matters most: on a Mac, Ash got Qwen 27B jumping from 20 to 88 tokens per second. That’s not merely a tweak… it’s a revolution!
But the reality on the ground is different. The unhobbling phase that researchers predicted — where efficiency beats brute force — is not merely coming. It is already happening, and Ash Hart is one of its grassroots architects.
The Unhobbling Is Real: How Batching and Speculative Decoding Rewrote the Rules
Here is the technical breakthrough that matters: Ash’s core insight was to stop treating a single-user workstation like an enterprise server. Instead of serving 32 concurrent streams like a data center rig, TensorFold (somehow) batches the draft lanes together so a single user goes dramatically faster. This is speculative decoding done right — using the model’s multi-token prediction head plus a DFlash drafter to rubber-stamp multiple guessed tokens per pass. The pre-fill time nearly doubled to just shy of 900 tokens per second. Decode lanes scaled to 16, 32, even 128 in some cases. The bottleneck now is draft depth — if Ash can predict eight or nine tokens deep, he believes he can hit 300 tokens per second on Qwen.
I have to pause here and note something that the mainstream AI press refuses to acknowledge. The entire industry narrative for the past three years has been about scaling — more parameters, more compute, more capital. But what Ash has demonstrated is that the opposite approach can reap huge rewards. Efficiency and raw horsepower matter more than raw horsepower alone. The compute famine that the establishment engineered, as I have documented extensively, is designed to strip you of power, AI, and freedom [2]. Ash’s work is a direct counter to that engineered scarcity. When a single developer can make a Mac outperform what enterprise hardware could do two years ago, the entire justification for centralized AI collapses.
The economics of this are devastating for the cloud AI cartel. Anthropic’s models now cost double previous versions, with a two-tier system that restricts high-risk queries, while the companies lose billions annually [3]. The entire revenue model of frontier AI depends on users being locked into expensive API calls. When a free, open-source engine runs on hardware you already own — and runs faster — that model dies. Ash didn’t just build an engine. He built an eviction notice for the cloud AI subscription economy.
A Single Developer Outrunning Teams of Engineers
The comparison that should make every AI investor nervous: VLLM and SGLang are maintained by large, well-funded teams with millions in backing. TensorFold is one man, and it runs selected models 2 to 2.5 times faster on DGX Sparks. Let that sink in. Ash’s DGX Sparks sat unused for three months before he ported the engine from Metal to CUDA. In that time, funded teams were still optimizing their Kubernetes orchestration. Ash was sleeping in his chair and shipping code.
I believe Jensen Huang owes this man a truckload of GPUs, and I am donating SSH access to one of my own DGX Spark boxes to back that up with action. The hardware economics here are striking. Software like TensorFold is why you cannot find Spark boxes anymore — the silicon became more valuable after launch because the software caught up. This is the opposite of the usual pattern, where hardware waits for software. Here, software unlocked hardware that the market had already written off. NVIDIA unveiled Project DIGITS as a personal AI supercomputer for the masses [4], and AMD launched the Ryzen AI Halo PC with 128GB memory at $3,999 to compete with the DGX Spark [5]. But neither company understood that the real unlock would come from open-source developers, not their own SDKs.
The lesson here is one I have learned repeatedly over years of building decentralized systems: open source beats headcount when one person refuses to give up. Ash archived his project three times. He did not quit. He did not pivot to a SaaS model. He did not raise venture capital. He kept working until the engine broke through. That kind of persistence cannot be bought, and it cannot be replicated by hiring more engineers. It can only be matched by other people who refuse to give up.
Living Weights: An AI That Learns, Unlearns, and Can Be Inherited
One more thing: Ash also built an experimental system where an LLM is given feedback and the weights shift. This is not fine-tuning. This is not LoRA. This is in-flight learning on a laptop without opening PyTorch. In Ash’s experiments, the model learned ‘my favorite color is blue,’ kept that knowledge across machines, and supports a unlearn command so bad knowledge can be removed. Think about what that means for a moment. An AI that can learn from its environment in real time, carry that learning across hardware, and selectively forget — this is not a chatbot. This is a new kind of cognition. The research is early, but promising.
Todd, a colleague of mine in the decentralized AI space, raised a question that has stayed with me: could grandchildren inherit an AI carrying 20 years of a founder’s accumulated wisdom? That question sounds like science fiction until you realize that Ash has already demonstrated the mechanism. If weights can shift in-flight and persist across machines, then the accumulated knowledge of a lifetime — the lessons, the mistakes, the corrected errors — can be transferred. A naturopathy-tuned Qwen variant trained on 20+ gigabytes of curated natural health text is now conceivable. This is the kind of breakthrough that terrifies centralized institutions, because it means that knowledge cannot be confiscated or controlled once it is embedded in weights that anyone can inherit.
Cortheon is the validation loop baked into TensorFold that lets a 4B model research the web and behave like a 35B model. This is the final piece. A small model that can research, validate, and behave like a large model — running locally, with no API calls, no censorship filters, no refusal mechanisms. I have written extensively about how the establishment is dumbing down AI on purpose [6], and how local, uncensored AI is the only path to lasting freedom [7]. Ash Hart’s living weights system is the technical implementation of that freedom.
Local AI as Infrastructure for Humanity — and a Shield Against Control
A woman in Russia used TensorFold to triple her medical document throughput. A patient got a diagnosis and treatment because of it. I want you to sit with that for a moment. This is not a benchmark. This is a human being whose life was profoundly impacted because an open-source engine ran on local hardware. HIPAA compliance becomes trivial when the model runs inside your own clinic. The entire compliance-industrial complex that surrounds cloud AI evaporates when the inference happens on hardware you physically control.
The UK’s NHS is on its knees. A local virtual doctor is an obvious, unbuilt win. But the establishment will never build it, because a local virtual doctor cannot be monetized by the same companies that profit from centralized control. I have argued that we are at a crossroads: either we embrace decentralized, locally run AI models that empower individuals, or we surrender to a centralized system where governments and Big Tech collude to ban open-source AI and concentrate power [7]. Ash Hart’s work is on the right side of that crossroads.
Prompt injection defense is another area where local AI wins. A separate decision engine like Jev or Laya as a second AI layer guarding your main LLM is far more effective than trusting a cloud provider’s guardrails. And on the question of refusals and censorship: cloud models blocked Ash from red-teaming his own CUDA-to-Metal DMA project. Only local models would help. This is the reality of centralized AI — it prevents you from even debugging your own code if the model decides your request is too dangerous.
I see machine cognition as infrastructure, like electricity or clean water. Guardrailed, centralized AI is an abomination. The plot to criminalize open-source AI and hand tech giants a government-protected cartel is already underway [8], and the only defense is to build and run local systems before the regulators catch up.
Stop Waiting for Permission: Run Your Own AI Today
Download TensorFold at tensorfold.dev. On a MacBook Pro, it is as easy as installing a GUI app. If you have a DGX Spark or equivalent hardware, the CUDA port is there waiting for you. Follow Ash at ashxhart on X. Support the builders — Mia AI Lab, Zach Vorhies’ Rust OBS rebuild, and the other developers who are working without institutional backing to make local AI a reality. The next six months will bring strategic, role-specialized models and further footprint reductions. Qwen Flash-Next is already a third the size of GLM at 80 to 85 percent of the intelligence. The trend line is clear: smaller, faster, more local.
I’ve predicted before that China’s open-source models are going to crush the U.S. AI industry and collapse the semiconductor bubble [9], and that the era of token abundance is coming [10]. Ash Hart’s TensorFold is the engine that makes that abundance possible on hardware you already own. The Anthropic backfire is already happening — corporations are racing to local open-source AI because they see the writing on the wall [11]. The compute famine is not going to stop this. The regulatory crackdown is not going to stop this. The only thing that could stop it is if people like you wait for permission instead of downloading the code and running it yourself.
My closing conviction: local AI is going to win. It will win because people like Ash Hart refuse to let three companies own human cognition. It will win because the economics of centralized inference are unsustainable. It will win because the technology is now good enough to run on your desk. The only question is whether you will be running it before the regulators decide you are not allowed to. The answer to that question is up to you.
Download the engine. Run the model. Own your own cognition. And watch all my episodes about decentralized technology at Decentralize.TV
References
A License for Your Brain: The Coming AI Crackdown and Why You Must Practice LLM Self Custody – NaturalNews.com, June 29, 2026. by NaturalNews.com
The Compute Famine Isn’t an Accident — It’s an Engineered Crisis to Strip You of Power, AI, and Freedom – NaturalNews.com, August 20, 2026. by NaturalNews.com
AI model costs skyrocket, raising questions about access and control – NaturalNews.com, June 27, 2026. by NaturalNews.com
NVIDIA unveils Project DIGITS a personal AI supercomputer for the masses – NaturalNews.com, January 09, 2025. by NaturalNews.com
AMD Introduces Ryzen AI Halo PC With 128GB Memory at $3,999, Targeting NVIDIA’s DGX Spark – NaturalNews.com, June 15, 2026. by NaturalNews.com
They Are Dumbing Down AI on Purpose ù Heres Why Its a Globalist Power Grab – NaturalNews.com, April 30, 2026. by NaturalNews.com
The Battle for Your Mind: Why Local, Uncensored AI Is the Only Path to Lasting Freedom and Decentralization – NaturalNews.com, June 03, 2026. by NaturalNews.com
The Plot to Criminalize Open Source AI and Hand Tech Giants a Government Protected AI Cartel – NaturalNews.com, September 14, 2026. by NaturalNews.com
Why China’s Open Source AI Will Crush the U.S. Industry and Collapse the Semiconductor Bubble – NaturalNews.com, July 02, 2026. by NaturalNews.com
The Era of Token Abundance Is Coming — and It Will Make Civilization Almost Unrecognizable – NaturalNews.com, September 24, 2026. by NaturalNews.com
The Anthropic Backfire: Why Corporations Are Racing to Local Open Source AI – NaturalNews.com, September 15, 2026. by NaturalNews.com
Mike Adams (aka the "Health Ranger") is the founding editor of NaturalNews.com, a best selling author (#1 best selling science book on Amazon.com called "Food Forensics"), an environmental scientist, a patent holder for a cesium radioactive isotope elimination invention, a multiple award winner for outstanding journalism, a science news publisher and influential commentator on topics ranging from science and medicine to culture and politics.
The agreement followed a meeting of G7 finance ministers and central bank governors held on the sidelines of the International Monetary Fund’s annual gathering in Bangkok. Katayama said G7 finance deputies had discussed the idea of tabletop exercises involving frontier AI, with the proposal subsequently approved at the ministerial level [1].
The plan will feature simulations developed by G7 finance authorities to test how governments and financial regulators respond to cyberattacks powered by advanced AI systems [2]. A Japanese finance ministry official who attended the leaders’ meeting told reporters on Oct. 15 that the exercises will test how financial authorities respond to AI-driven cyberattacks.
IMF Cites Risk to Confidence and Markets
The agreement came after the IMF warned this week that a major AI-enabled cyberattack on financial institutions or critical services could undermine confidence, which would then ripple through global markets. In an Oct. 13 blog post, the IMF stated that frontier AI models could accelerate both attacks and defenses, increasing the importance of cyber resilience, incident reporting, crisis preparedness and oversight of critical third-party providers.
The IMF reported that in the reported cyberattack cases so far this year, software providers had almost no time to patch vulnerabilities before attackers exploited them, compared with close to 300 days in 2021. That compression underscores the speed at which AI-enabled tools can identify and leverage weaknesses in software.
A separate IMF blog post published Oct. 15 said AI adds urgency by accelerating vulnerability discovery, exploitation and attack, compressing the attack-defense cycle to machine speed. The post stated that a major attack affecting payments, trading or deposit access could cause immediate losses and undermine confidence in the financial system.
The IMF recommended strengthening cyber defense capabilities, including testing financial institutions’ resilience.
Bank of England Says Recovery Planning Needed
Bank of England Deputy Governor Sarah Breeden said Thursday that the institution is working with banks to help prepare to recover from AI-empowered cyber breaches. Speaking at the annual meeting of the Institute of International Finance in Bangkok, Breeden said AI poses a systemic risk to financial systems through technological advancement.
Breeden said it is no longer enough for financial bodies to assume cyberattacks will not get through, and that recovery options are required if institutions are hit. She described cyber as the thing that keeps her up at night and said she worries most about waking up to find a systemically important bank or core infrastructure paralyzed.
Her comments align with the IMF’s emphasis on crisis preparedness and incident reporting. The Bank of England’s work with banks on recovery planning reflects a shift from prevention alone toward resilience and continuity planning in the event of a successful breach.
Oversight of Third-Party Providers Draws Attention
The IMF blog posts referenced oversight of critical third-party providers as a component of cyber resilience. That focus reflects concerns that attackers may target software suppliers or other outside vendors to reach financial institutions indirectly.
Reported cases this year indicated attackers exploited vulnerabilities faster than providers could patch them, according to the IMF. The IMF’s Oct. 15 post described a compressed attack-defense cycle operating at machine speed. The Bank of England said it is working with banks on recovery planning rather than assuming breaches will be prevented.
Next Steps Remain to Be Defined
The exercises would involve G7 finance ministries and central banks and could extend to private financial institutions, according to the Japanese finance ministry official. No timetable, format or list of participating institutions for the exercises was announced in the statements reviewed.
The agreement was announced during the IMF’s annual gathering in Bangkok, where finance ministers and central bank governors met. The plan will feature simulations developed by G7 finance authorities to test how they can respond to AI-driven cyberattacks [2].
Reuters contributed to the report.
References
G7 Plans Exercises to Counter AI Cyber Attacks – StratNews Global. https://stratnewsglobal.com/technology/g7-plans-exercises-to-counter-ai-cyber-attacks/
G7 to launch exercises to guard against AI cyber attacks. https://www.reuters.com/world/asia-pacific/g7-launch-exercises-guard-against-ai-cyber-attacks-2026-10-16/